
Outline
- Introduction
- Key terminology used in a virtual network
- Lab 1: Create a virtual network using Azure Portal
- Lab 2: Create a virtual network using Azure CLI
- Lab 3: Create a virtual network using PowerShell
- Lab 4: Create a virtual network using ARM template
Introduction
In this article, we will go through the concept of Azure virtual network, what Azure virtual network is and terms in the virtual network which are used to create a virtual network.
Key terminology used in a virtual network
- Virtual Network
- IP Address
- Subnet
- Network Interface Card
- Load Balancer
- Application Gateway
- Traffic Manager
- Network Security Group
- Force Tunnelling
- Regional Virtual Network
- Cross Premises Network
Virtual Network: Virtual network (VNet) is your private network in the Azure cloud. This provides you with a secure way to communicate between your virtual machines and other services that are inside of your virtual network in Azure Cloud or on-premises.
IP Address: IP addresses are the range of addresses that define the network and each VM which is part of a virtual network can communicate through this IP address. Each VM within the Vnet can have a private or public IP address, the private IP address allows communication between one or more of the VMs inside the Vnet, but from outside of the Vnet public IP address is used over the internet for communication.
Subnet: It is a network inside your network. In other words, Subnet is a small portion of the IP address range that is allocated to a virtual network.
Network Interface Card: The Network interface card is used to connect the VM through the network.
Load Balancer: Load balancer is used to distribute the incoming traffic evenly across a group of servers. This distribution of traffic is based on the health probe of servers that are behind the load balancer.
Application Gateway: It is a web traffic load balancer that helps you to manage your traffic to your web application. It is on top of load balancing your workloads, so it can make routing decisions to pass your URL request to the appropriate node. For example, if two types of requests come to the application gateway, one is for images and the second one is for videos, then the application gateway can make a decision where to redirect these requests if we have two dedicated servers, one for serving images and one for serving videos.
Traffic Manager: It is also used to distribute the traffic at the DNS level, for example, if I have a website www.IamCkNitin.com and I have traffic from many countries and to manage and I want to distribute the traffic to manage the load in a way that US traffic should go through the US server and India traffic should go through the India server.
Network Security Group: It's a set of rules that work as a filter for your traffic that connects with the Azure virtual network (Vnet). It allows or denies inbound network security network traffic.
For example, if we have a Vnet “XYZ” and there are two VMs “A” and “B” inside the Vnet “XYZ” and we don’t want an RDP connection to access these VMs through the public IP but both the machines can access their RDP using their private IP, then we can define this type of security under the Network Security Group.
Force Tunnelling: Force tunneling controls the flow of your traffic, it is for inspection and auditing of all internet-bound traffic. It forces all your internet-bound traffic to your on-premise location via sit-to-site VPN tunneling so you can have the ability to inspect and audit the traffic.
Regional Network: Microsoft Azure has multiple regions. We may have multiple Vnets that may work in different regions, so the connections between these Vnets which are in different regions come under this section.
Cross Premises Network: It is a network that is connected to your on-premise network. It allows your Azure virtual machine to be part of your on-premise network.
Lab 1 - Create a Virtual Network Using Azure Portal
- Log in to Azure portal
- In the search bar “Virtual Network” select it
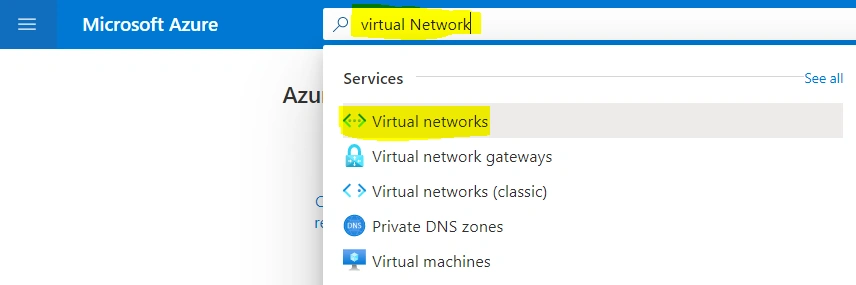
Figure 1. - Now click on the “+ Add” to start creating a virtual network
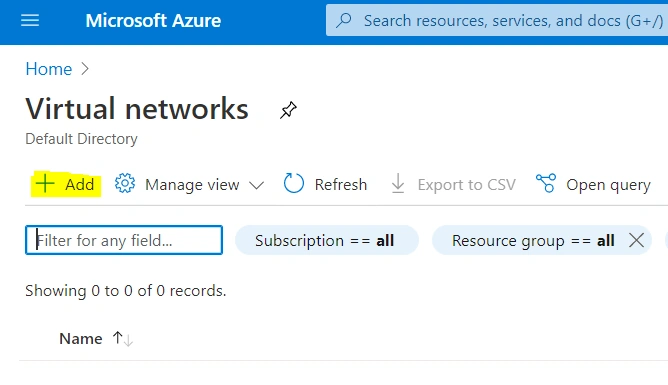
Figure 2. - Enter the basic details for the virtual network
The first tab, “Basic” is for adding basic details for the virtual network
-
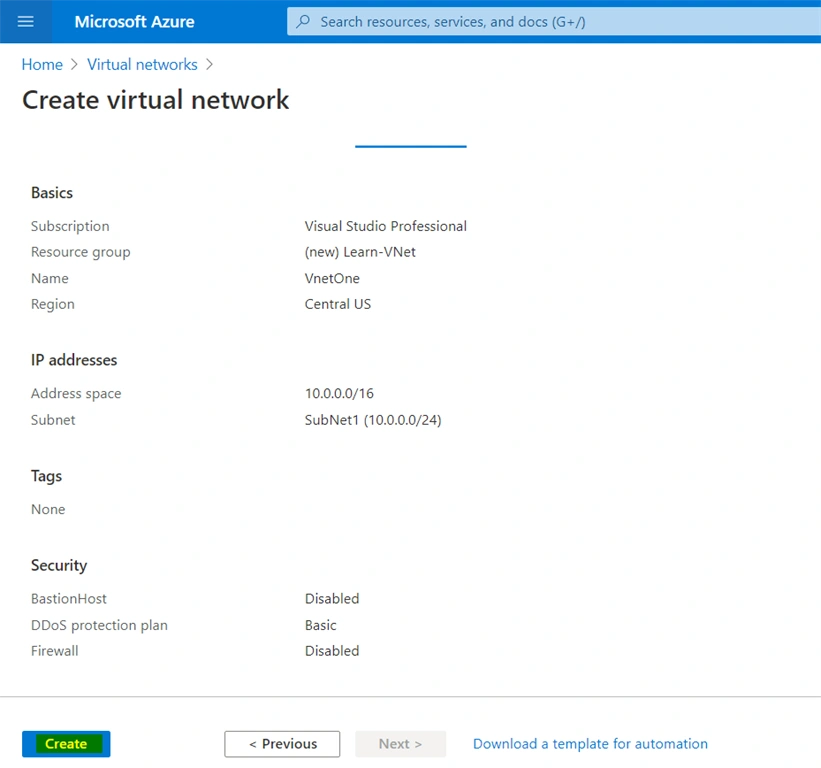
- Subscription: “Visual Studio Professional”
- Resource Group: If you have an existing resource group then you can select it, I created a new one called “Learn-Vnet”
- Name: VnetOne
- Region: You can select any region; in this lab I am going to select “(US) Central US”
- Either Click “Review + Create” or you can click “Next: IP Addresses”
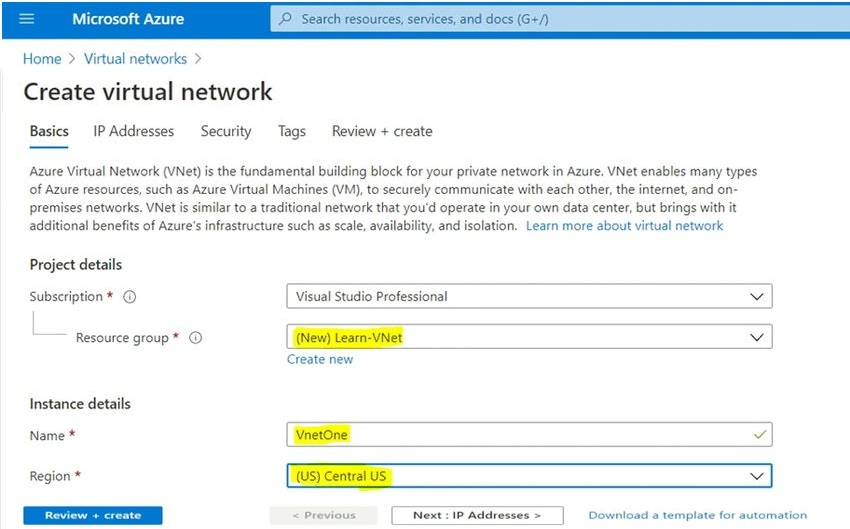
Figure 3.
- Ipv4 address space By default, an address space is automatically created. You can click the address space to adjust it to reflect your values. You can also add additional address space
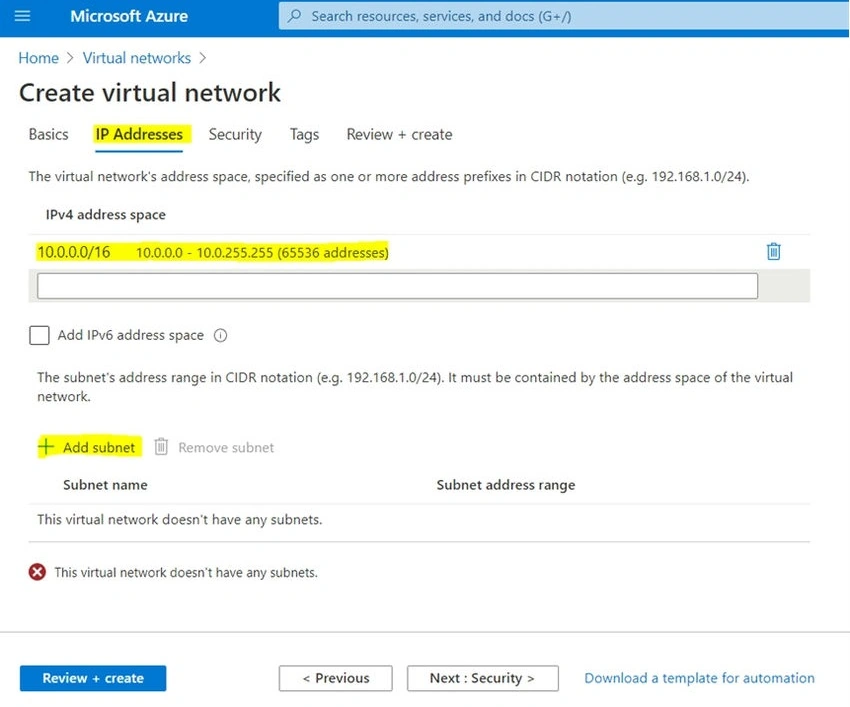
Figure 4. - Subnet: If you use the default address space, a default subnet is created automatically. If you change the address space, you need to add a subnet. Select + Add subnet to open the Add subnet window. Configure the following settings and then select Add to add the values.
- Subnet name -In this example, we named the subnet “SubNet1”.
- Subnet address range -The address range for this subnet.
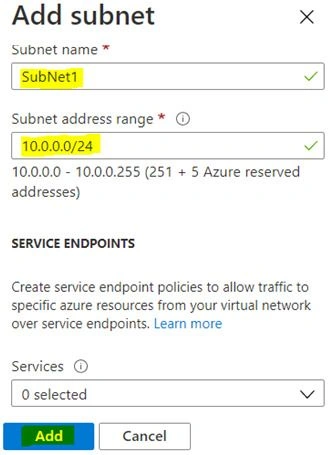
Figure 5.
- On the Security tab, at this time, leave the default values,
- BastionHost: Disable
- Ddos protection standard: Basic
- Firewall: Disabled
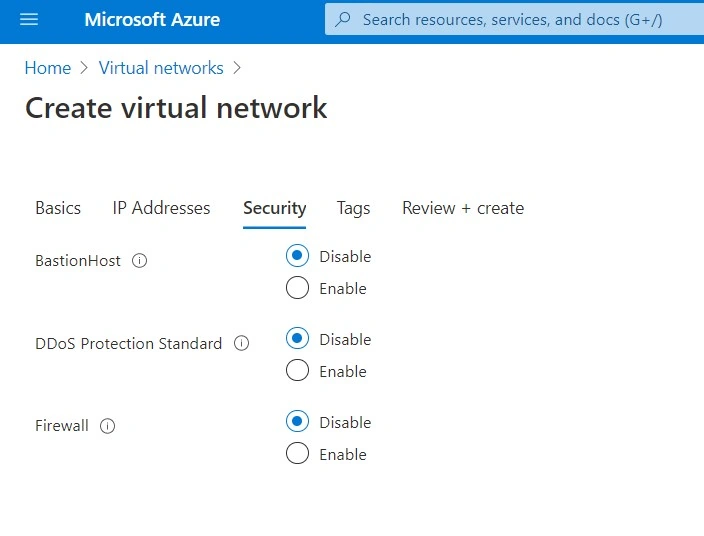
Figure 6.
- Leave the tag details empty
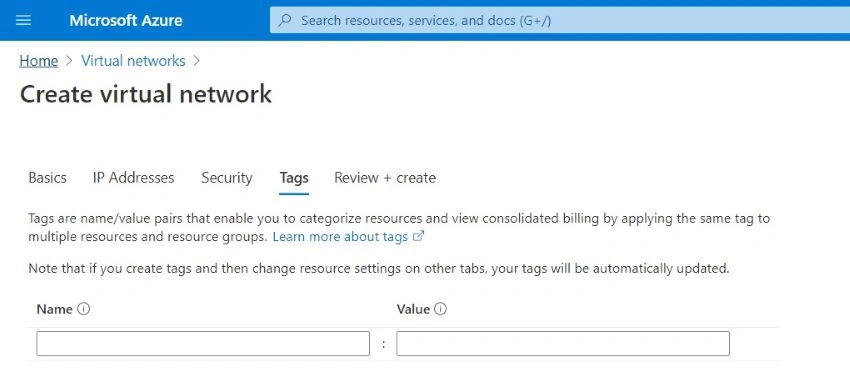
Figure 7. - Select Review + Create to validate the virtual network settings.
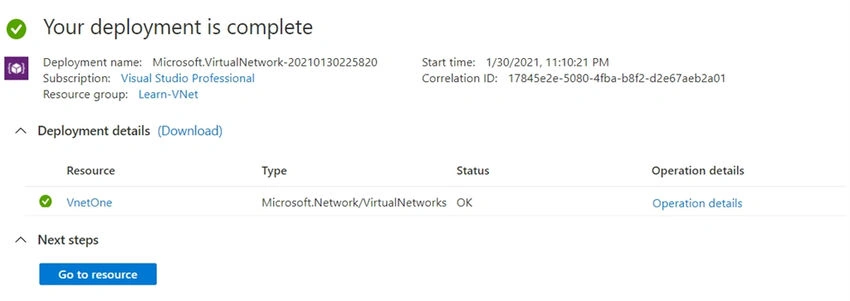
- After the settings have been validated, select Create when you hit the Create button your virtual network will be created.
Note: If want to save this information as a template for future use you can click the “Download as a template for automation” as shown highlighted in Figure 8.
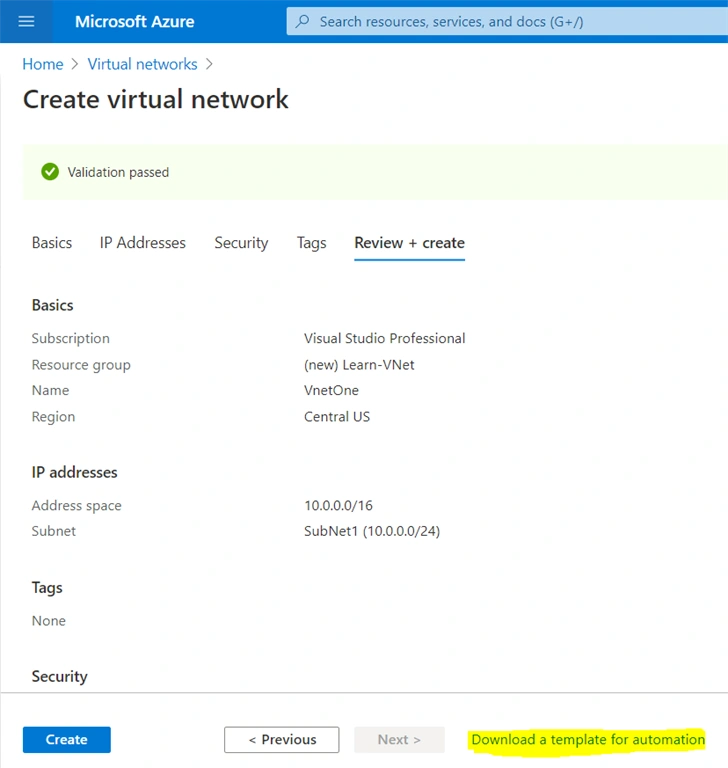
Figure 8.
- Click the “Download” to download this JSON template as shown in Figure 9
- Or you can add it to your library
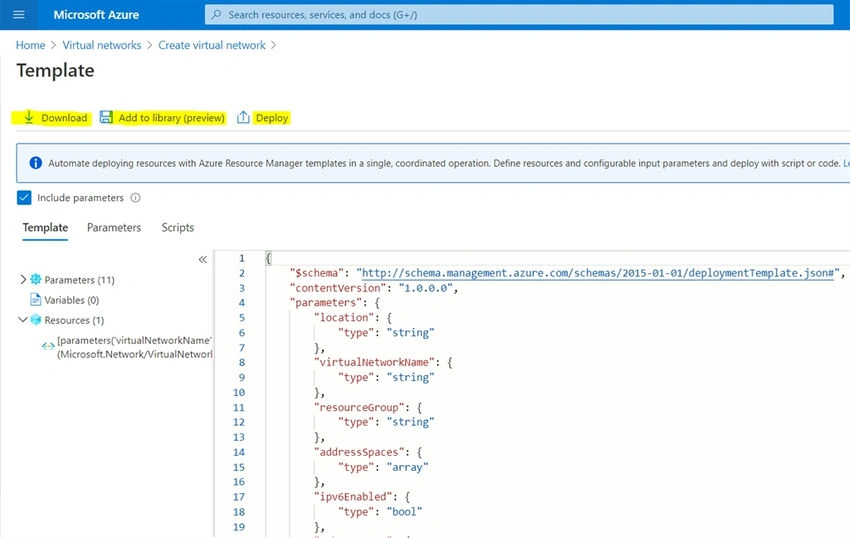
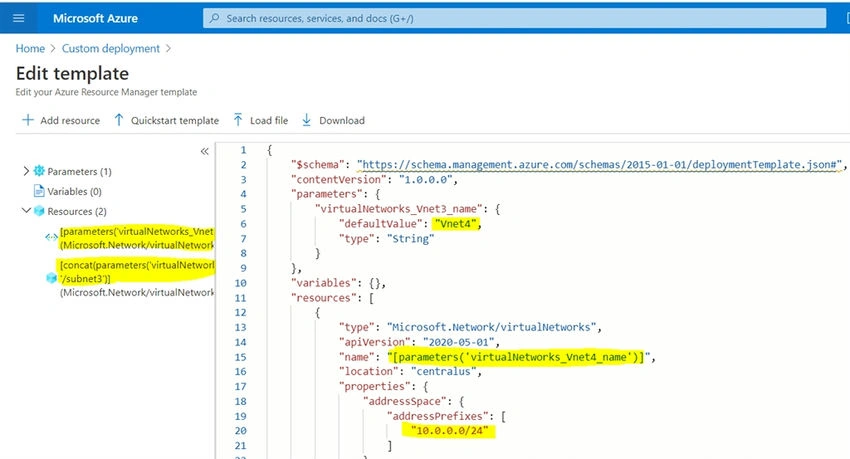
Figure 9.{ "$schema": "http://schema.management.azure.com/schemas/2015-01-01/deploymentTemplate.json#", "contentVersion": "1.0.0.0", "parameters": { "location": { "type": "string" }, "virtualNetworkName": { "type": "string" }, "resourceGroup": { "type": "string" }, "addressSpaces": { "type": "array" }, "ipv6Enabled": { "type": "bool" }, "subnetCount": { "type": "int" }, "subnet0_name": { "type": "string" }, "subnet0_addressRange": { "type": "string" }, "ddosProtectionPlanEnabled": { "type": "bool" }, "firewallEnabled": { "type": "bool" }, "bastionEnabled": { "type": "bool" } }, "variables": {}, "resources": [ { "name": "[parameters('virtualNetworkName')]", "type": "Microsoft.Network/VirtualNetworks", "apiVersion": "2019-09-01", "location": "[parameters('location')]", "dependsOn": [], "tags": {}, "properties": { "addressSpace": { "addressPrefixes": ["10.0.0.0/16"] }, "subnets": [ { "name": "SubNet1", "properties": { "addressPrefix": "10.0.0.0/24" } } ], "enableDdosProtection": "[parameters('ddosProtectionPlanEnabled')]" } } ] }
MM JAckPosted Jul 17, 2024, 9:53 AM
Nyce Article
Mayooran NavamanyPosted Feb 5, 2024, 4:47 PM
That is a nice good explanation.
Hamid KhanPosted Feb 27, 2021, 7:48 PM
Very very good explanation.............