
Introduction
The Default SPO admin center provides an option to restrict the access of the complete SPO tenant based on the network/location. Restricting a particular Site collection with the SPO admin center isn’t possible. However, this can be achieved by integrating SPO with Azure Active Directory. The Conditional Access feature of Azure Active Directory premium helps to restrict a particular site based on the device platforms, locations, client apps, and device state.
Configuring Trusted IPs
The organization’s IP should be marked as Trusted IPs in Azure in order to have uninterrupted and easily manageable connection with the Azure and Office365 Services.
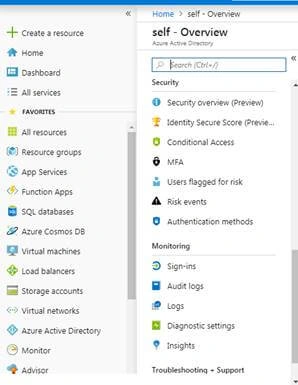
- Login to Azure Portal, click on Azure Active Directory in the right pane, and select "Conditional Access" from the Azure Active Directory Blade.
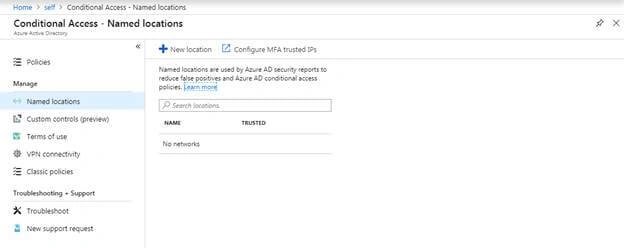
- Click on "Named Locations".
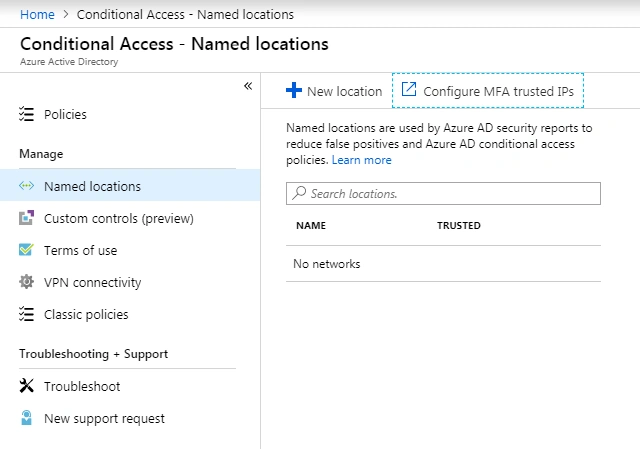
- Click on "Configure MFA trusted IPs".
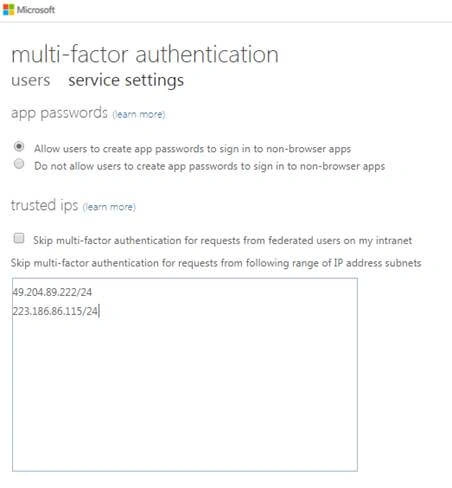
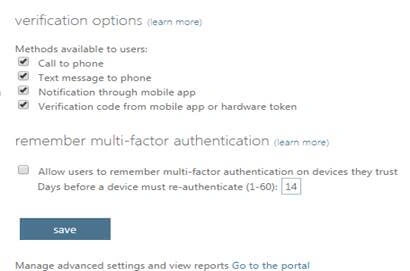
- In Multi-Factor Authentication page, in Trusted IPs, specify the IP address subnets of the organization and/or the IP address subnets which can be trusted by the Azure and Office365 services.
- Click "Save".
Configuration of Conditional Access
The Azure AD Conditional Access is part of Azure AD Premium P2 License.
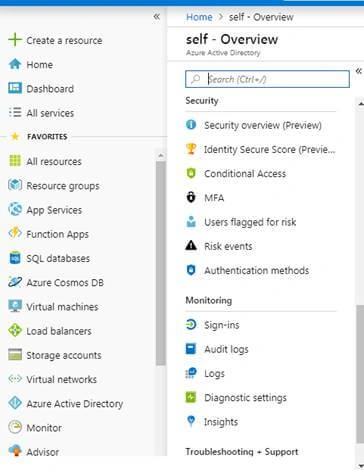
- Login to https://portal.azure.com/ and navigate to Azure Active Directory.
- Select "Conditional Access" from Azure Active Directory blade.
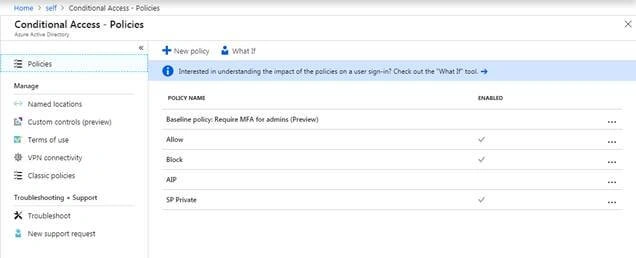
- Select Policies and click on "New Policy".
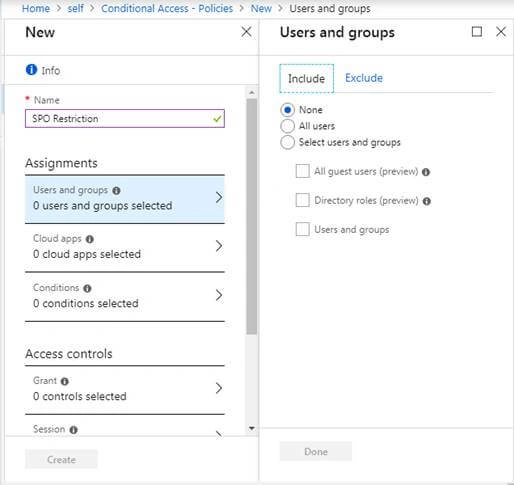
- Specify the Policy Name & select “Users and Groups”.
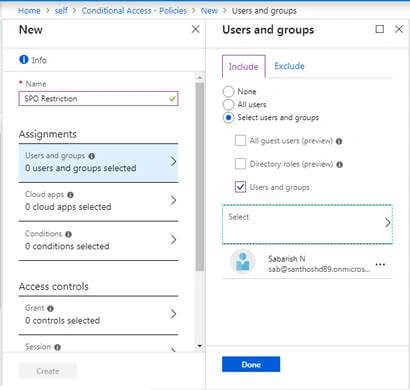
- Include\Exclude the users for whom the restrictions should be applied.
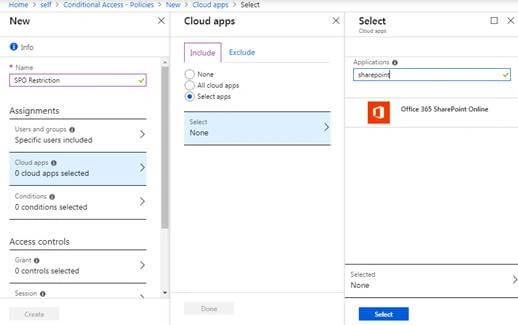
- Click on Cloud Apps, select “Select Apps”, and search for “SharePoint Online” in the Application Gallery.
- Double-click on Office 365 SharePoint Online and click.
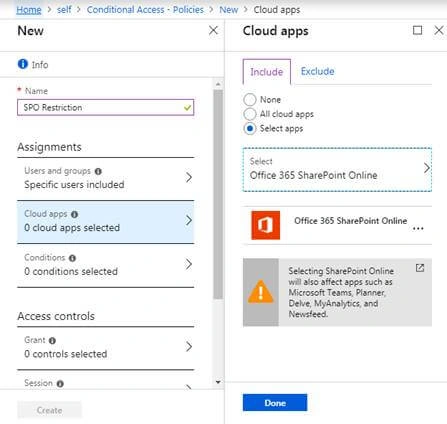
- Click "Done".
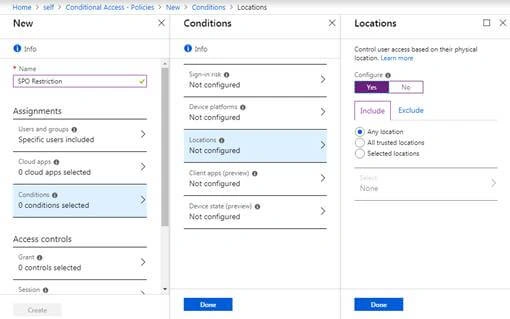
- Click on Conditions and select Locations.
- Click "Yes" to configure the location-based access.
- In the Include tab, select "Any Location".
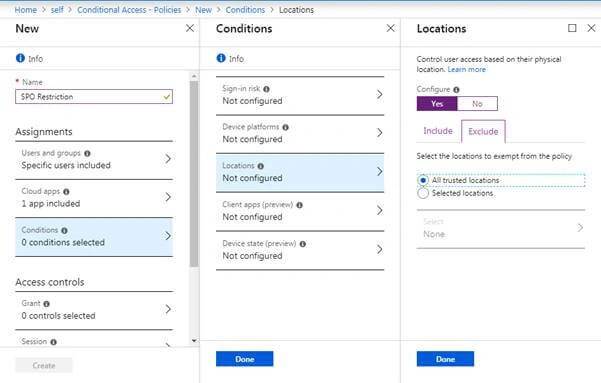
- In the Exclude tab, select "All Trusted locations".
- Click "Done".
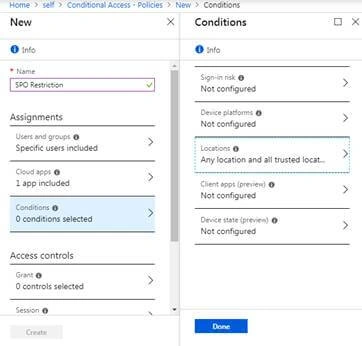
- Click "Done".
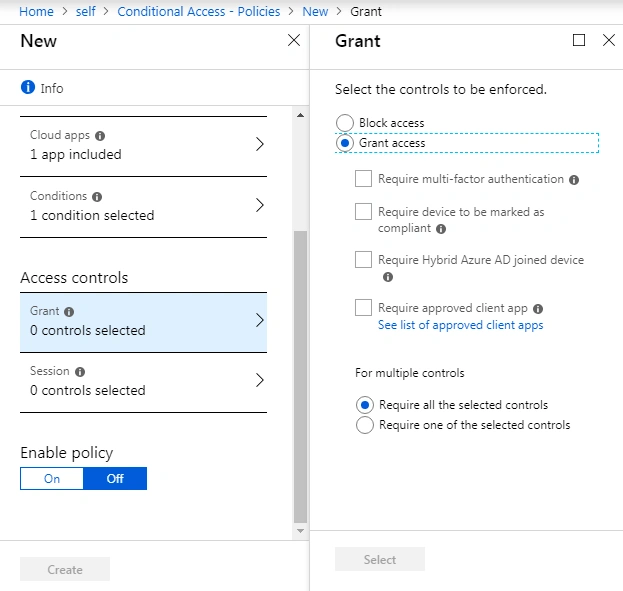
- In Access Control, click "Grant Access".
Note
No changes are required on the option which is selected by default.
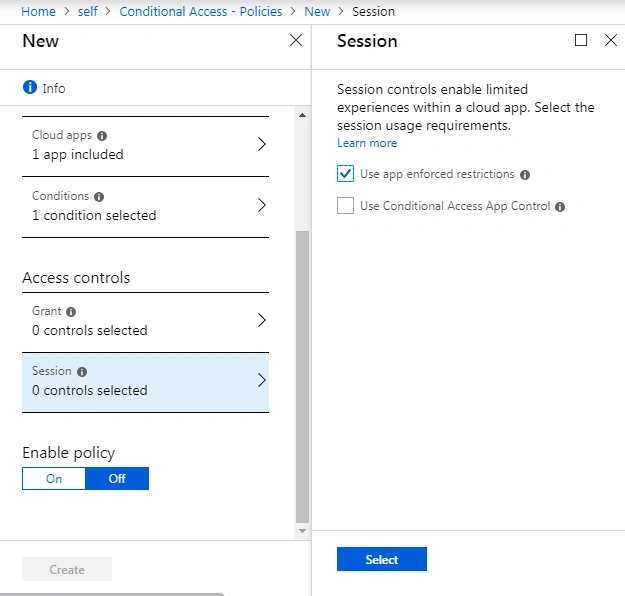
- Click on "Session" and select "Use App Enforced Restrictions".
By selecting “Use App Enforced Restrictions”, the configuration settings of subsite collections will work along with the conditional access to manage the Access Controls of individual subsites.
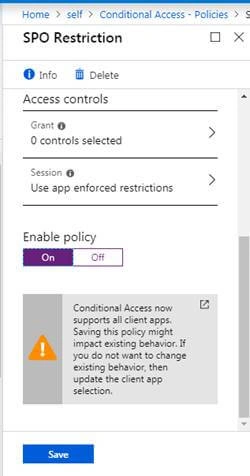
- Select ON in the "Enable Policy" section.
- Click "Save".
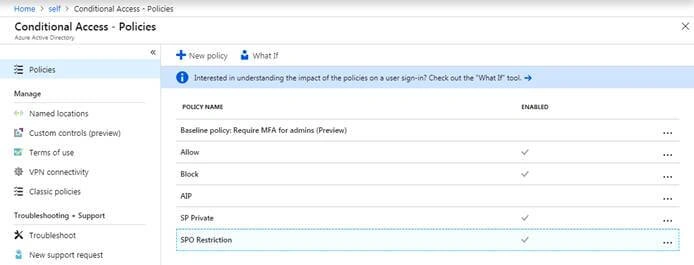
- Once the policy is created, it appears in the "Policies" tab of Conditional Access.
Access Restriction for specific Site
The final step is to update the configuration settings of the subsite for which the access restriction has to be applied.
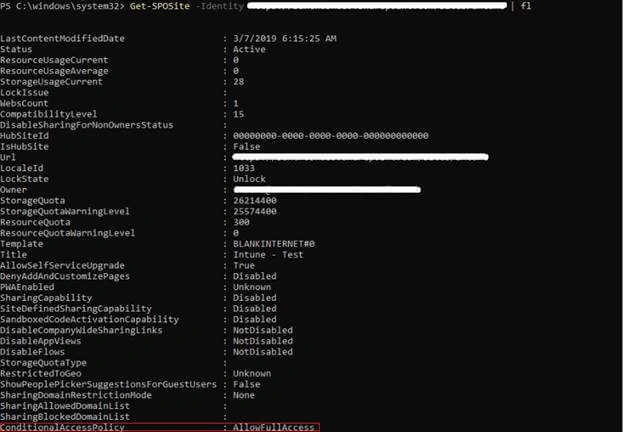
- Login to SharePoint Online Administrator PowerShell.
- Run the below command to check the existing configuration settings of the subsite.
Get-SPOSite –Identity <Subsite URL> | fl
“Note that the Conditional Access Policy is set to Allow FullAccess”.
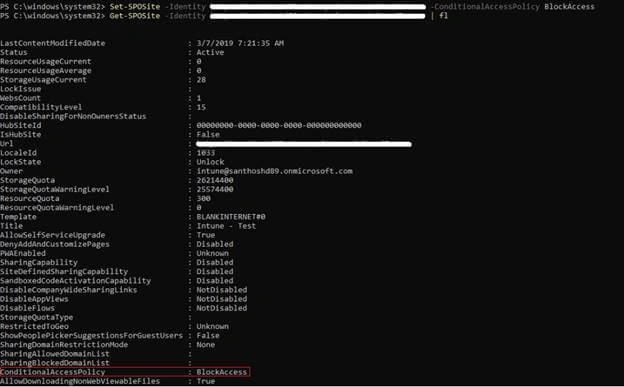
Run the below command to block access for a particular site using conditional access.
“Set-SPOSite –Identity <Subsite URL> -ConditionalAccessPolicy BlockAccess”
Sajith G HPosted Aug 12, 2021, 12:38 PM
I followed the same step. Unfortunately it is not working