
Introduction
In this article, we will explore how to create a flow with Power Automate to break inheritance permissions on list item-level SharePoint Lists and add roles (new permissions).
For that, we are going to use the REST API of SharePoint.
Power Automate has been enhanced and you might find an action directly to accomplish this task. There's no other solution at the time, however, than using the SharePoint REST API.
We can also check one by one:
- Break inheritance on list item-level List
- Add list item-level roles(new permissions)
Break inheritance on list item-level List
We are going to define custom permissions for list item level, and we are going to have to break the inheritance role. This will not change permissions but will simply change the current users into 'specified' permissions instead of 'inherited.'
We will see step by step how to implement it with Power Automate.
http://[SHAREPOINT_SITE_URL]/_api/web/lists/getByTitle('[LIST_TITLE]')/breakroleinheritance(copyRoleAssignments=true, clearSubscopes=true)
As you can see, in the URL I have "copyRoleAssignments = true," if set to true, this means it copies the parent's roles / permissions, if set to false, it does not copy the parent's roles / permissions.
Add list item-level roles (new permissions)
The permissions had to be removed and set in such a way that only a particular Group or user such as Created by or Modified by would have access to them for review and administration purposes. In other words: We had to break the inheritance of the default permission and set up unique permissions at item-level list.
Then following REST API to Add list item level roles/ permission
http://[SHAREPOINT_SITE_URL]/_api/web/lists/getByTitle('[LIST_TITLE]')/roleassignments/addroleassignment(principalid=[GROUP_ID/User_ID],roleDefId=[ROLE_ID])
The step by step Flow action to build
We have created an Employee information list for adding new candidate's information and submitted it to HR Approval Group For approval. After submitting, the submitter candidate assigns read-only permission to his created record and HR Approves groups assigned with contribute permission.
Step 1
Go here and log in with your Office 365 account.
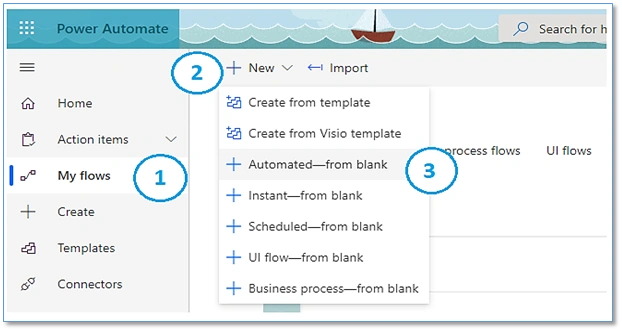
We start with a blank canvas and build the Flow ourselves. Therefore, click the +New button and select “Automated – from blank, follow the numerical points, as shown in the below screenshot,
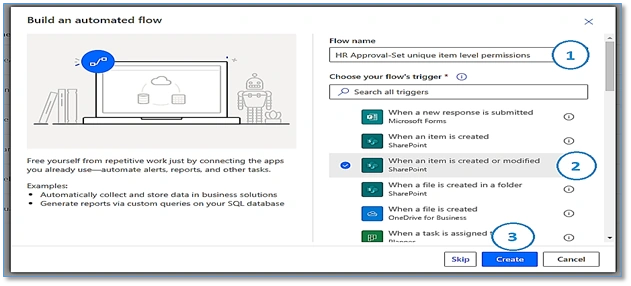
Provide a name and choose which Flow will trigger (or start). In our case this will be “When an item is created or modified” then click the Create button. Follow the numerical points, as shown in the below screenshot,
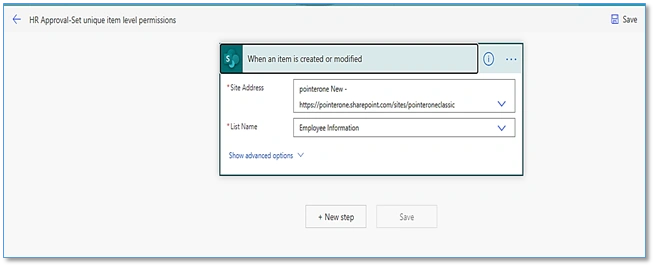
Enter the site address (URL) and select the list on which you want this Flow to run,
Step 2
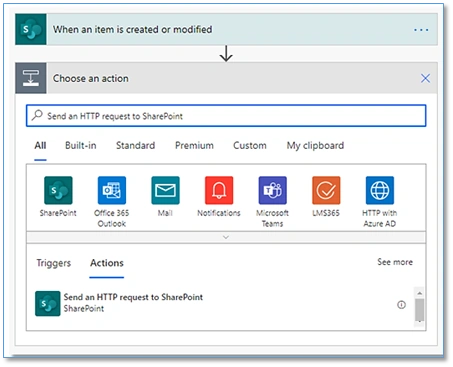
Click  the button below this first step to add a new action in the Search box by typing “Send an HTTP request to SharePoint” in the search bar and find the following action: “Send an HTTP request to SharePoint. This action will break the permissions inheritance of the list item and remove all permissions from it.
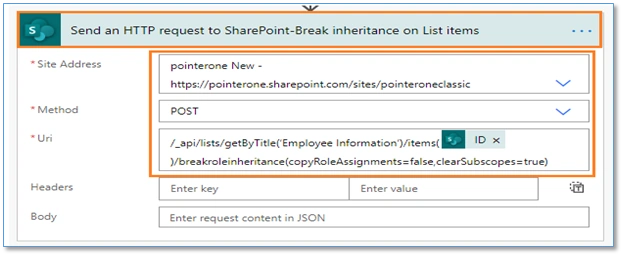
Configure the action parameter as follows,
| Site Address: the site URL. |
| Method: select “POST”. |
| Uri: _api/lists/getByTitle(Employee information ')/items(['ID'])/breakroleinheritance(copyRoleAssignments=false, clearSubscopes=true) |
This request contextualizes the SharePoint REST API and focuses on dynamic list item ID.
Step 3
We want to assign permissions to a specific group of people and Created by, so they can access the item. We need the Created by user's principal id. Add another “Send an HTTP request to SharePoint” action.
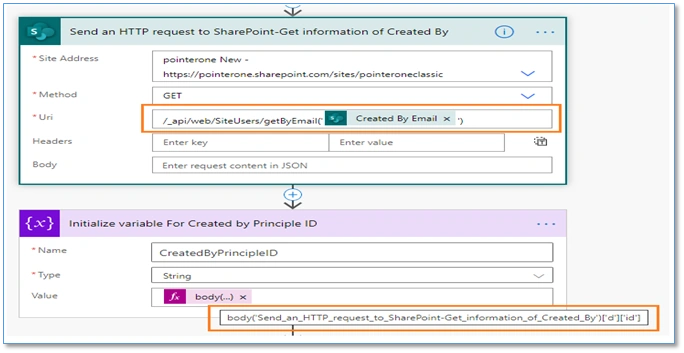
We have already created the HR Approved SharePoint group with the right people in it. Now we will grant that group access and assign it a permission level.
To do so, add another “Send an HTTP request to SharePoint” action. This part looks at the site groups and retrieves the group you specify,
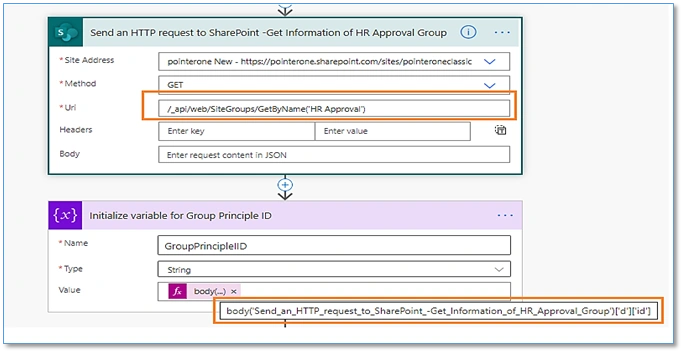
Step 4
Here we are going to give Created by user read permissions and HR Approved Members group the Contribute permissions on my list item. To do so, add another “Send an HTTP request to SharePoint” action.
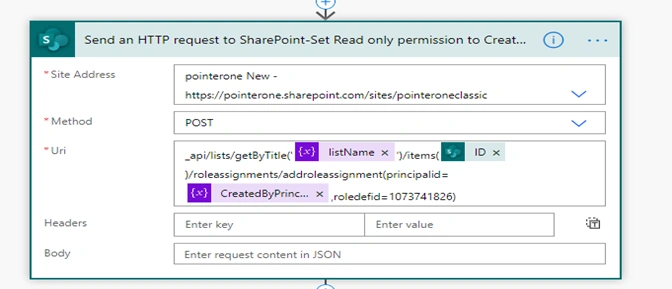
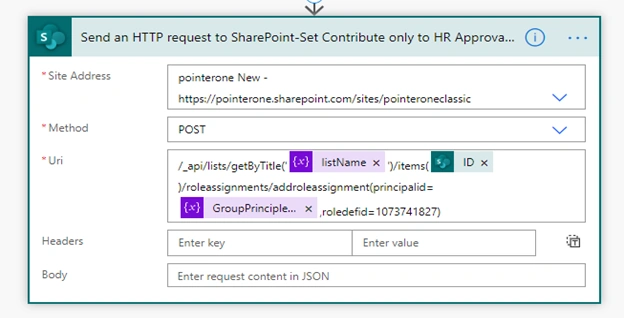
To assign item level permission we need to have the role definition ids. Here are a few out of the box ids below.
| Role Definition Name | Role Definition Id |
| Full Control | 1073741829 |
| Design | 1073741828 |
| Edit | 1073741830 |
| Contribute | 1073741827 |
| Read | 1073741826 |
| View Only | 1073741924 |
| Limited Access | 1073741825 |
O/p
Before breaking inheritance and setting list item-level permissions,
After breaking inheritance and setting list item-level permissions,
Note
- It is considered a best practice to give a clear descriptive name in the action header in order to improve readability and administration of the Flow. You can customize this by clicking on the right side of the header on the three horizontal dots (ellipsis) and then selecting "Rename."
- This is very important to note because if you add permissions, it will add permissions, but it will not replace other permissions
Sangay ChodenPosted Nov 29, 2021, 5:17 AM
Hi Author ...This is what I have been exactly wanting to do, towards the end of the flow how did you make the List Name dynamic ? Can you share the details of it pleaseee...will really help me.
deeksha kukretiPosted Mar 17, 2021, 10:06 AM
When we added permission to groups they got the correct permissions but the user whose connection we are using is also getting the full permission of the sharepoint item created using flow
Nikita KocharPosted Jan 8, 2021, 10:10 AM
How to get role definition Id for other roles?
vijay prajapatiPosted Sep 9, 2020, 8:00 AM
Can i add permission to specific user , not group and created by i need to set permission for user
CariaPosted Aug 28, 2020, 1:25 PM
I have a flow which is manually kicked off by users (not automatically) and runs an approval process, towards the end it does the steps above, breaking permissions and then setting SharePoint group permissions. At the break inheritence step is says access denied when a user with contribute rights starts the flow. If I , an admin run the flow it works. Thoughts? It is using the Flow connection, and the Flow account is in the owners account on the site.
Yahiya IqbalPosted Jun 19, 2020, 3:11 PM
Thanks for the replay I used %20 instead of space it worked. Very strange but it worked. Thanks again!!!
Yahiya IqbalPosted Jun 13, 2020, 8:52 PM
Am getting below error {"error":{"code":"-1, System.Collections.Generic.KeyNotFoundException","message":{"lang":"en-US","value":"The given key was not present in the dictionary."}}} , Please note I am trying to add group to list permissions. My URL _api/web/lists/getbytitle('Private info')/roleassignments/addroleassignment(principalid=96,roleDefId=1073741931)