
Introduction
Azure Point-to-Site (P2S) VPN provides a secure way for client devices to connect to an Azure Virtual Network, granting access to private resources and Azure workloads. In this article, I will guide you through setting up a P2S VPN with certificate-based authentication, ensuring a secure and efficient connection for your clients.
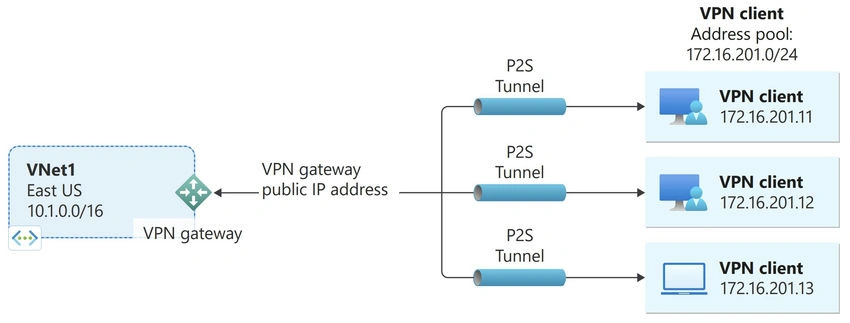
Overview Architecture of Azure Point-to-Site VPN
Prerequisite
- Azure Subscription
- Azure Virtual Network
- Azure VPN Gateway
- Client User Node Windows or Linux
Generate and export certificates for point-to-site using PowerShell
Step 1. Open PowerShell as an Administrator and launch PowerShell on your client PC with elevated permissions.
Step 2. Create a Client Root Certificate by running the following PowerShell script to generate a self-signed root certificate, as outlined in the official Microsoft documentation
$params = @{
    Type = 'Custom'
    Subject = 'CN=P2SRootCert'
    KeySpec = 'Signature'
    KeyExportPolicy = 'Exportable'
    KeyUsage = 'CertSign'
    KeyUsageProperty = 'Sign'
    KeyLength = 2048
    HashAlgorithm = 'sha256'
    NotAfter = (Get-Date).AddMonths(24)
    CertStoreLocation = 'Cert:\CurrentUser\My'
}
$cert = New-SelfSignedCertificate @params
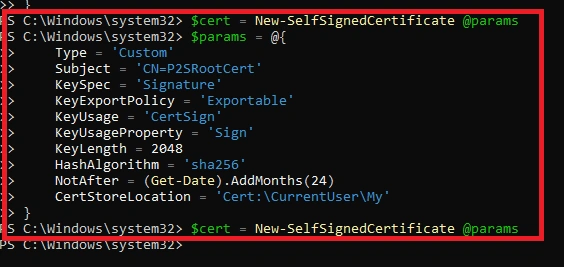
Note Replace "P2SRootCert" with your desired certificate name. However, the certificate is valid for 5 years by default.
Step 3. Create Client Certificates To create client certificates use the below script.
$params = @{
       Type = 'Custom'
       Subject = 'CN=P2SChildCert'
       DnsName = 'P2SChildCert'
       KeySpec = 'Signature'
       KeyExportPolicy = 'Exportable'
       KeyLength = 2048
       HashAlgorithm = 'sha256'
       NotAfter = (Get-Date).AddMonths(18)
       CertStoreLocation = 'Cert:\CurrentUser\My'
       Signer = $cert
       TextExtension = @(
        '2.5.29.37={text}1.3.6.1.5.5.7.3.2')
   }
   New-SelfSignedCertificate @params
Successfully created both my certificates.

Steps to Export the Root Certificate Public Key (.cer)
Step 1. Open Manage User Certificates by pressing Win + R, typing certmgr.msc, and pressing Enter.

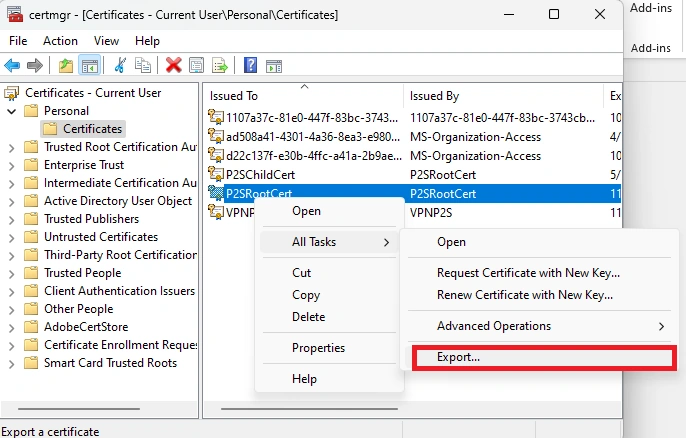
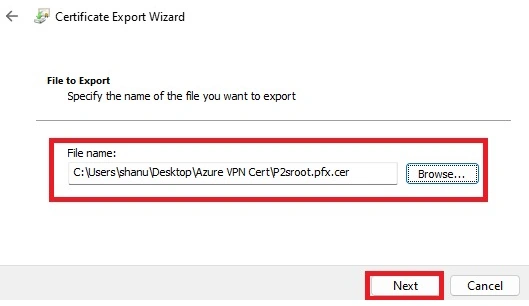
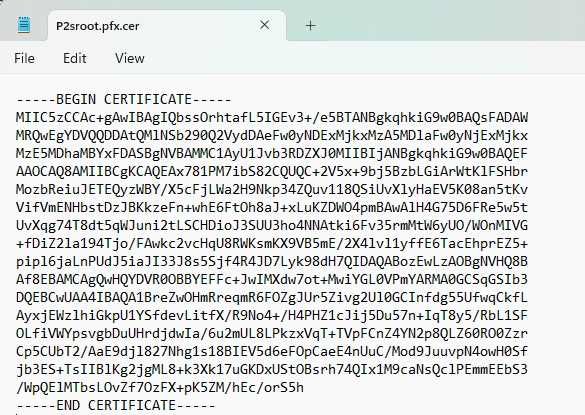
Step 2. Navigate to Certificates - Current User > Personal > Certificates. Locate your self-signed root certificate, right-click it, and select All Tasks > Export.





Join the conversation! Your thoughts help the community grow.