
Introduction
In this article, we are going to learn how we can deploy an apache server to both public and private subnets in AWS. so first we create two EC2 instances one if public and another one is a private EC2 instance and then we can deploy the apache server to these instances. First, we understand what is -
- Public instance - can be accessible from the internet which means this can be accessed from anywhere.
- Private instance - can not be accessible from the internet directly which means nobody can enter this subnet directly, generally, we put database servers in private instances and they can access via NAT gateway that resides in public subnets.to use the NAT gateway we require VPC
- VPC - Virtual Private Cloud(VPC) is a secure, isolated private cloud hosted in a public cloud
Create a new VPC in AWS
Four steps to creating a new VPC,
- Create a VPC
- Create subnet
- Create an internet gateway
- Define route table
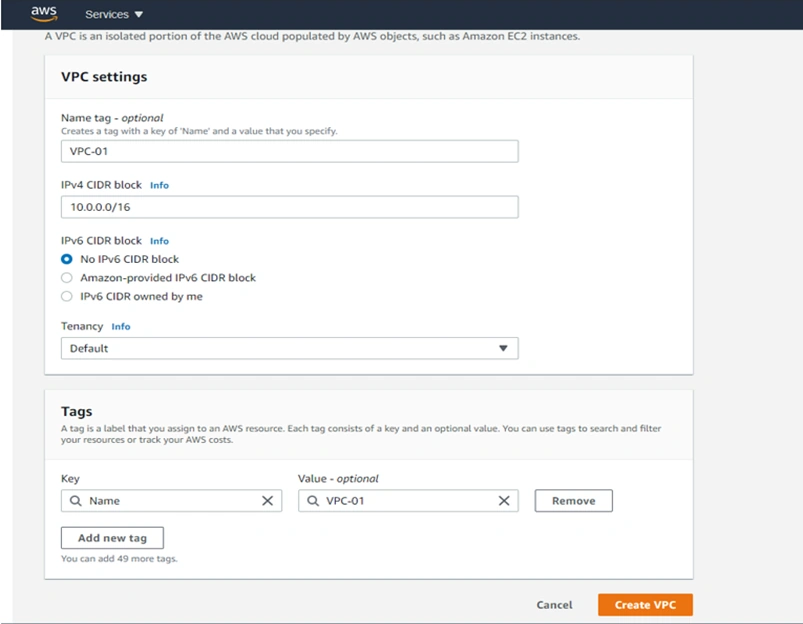
Create VPC - Give the VPC name and choose the IPv4 CIDR block which basically used for allocating IP addresses
Create one public and private subnet
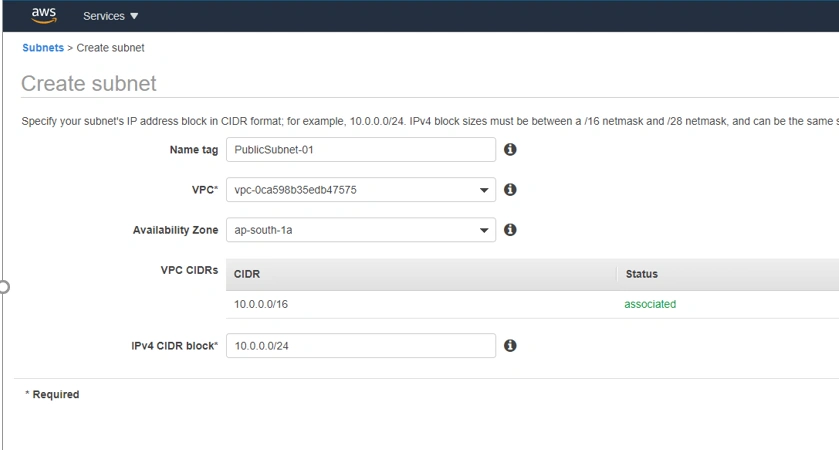
Public Subnet - Choose the name tag and select the VPC which we create in the last step and the availability zone,
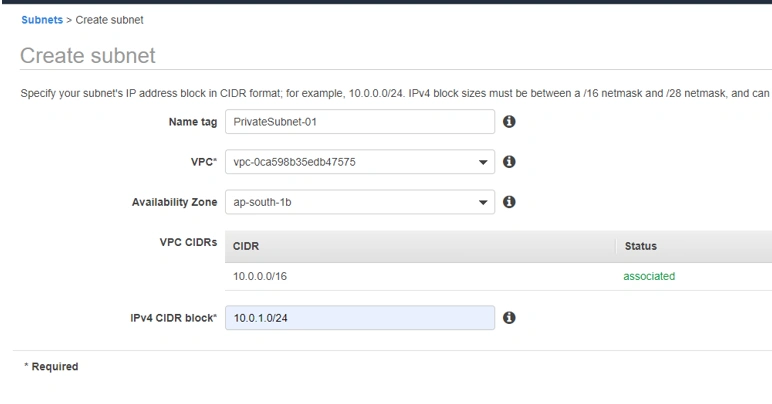
Private Subnet - Similarly create one more subnet for the private subnet.
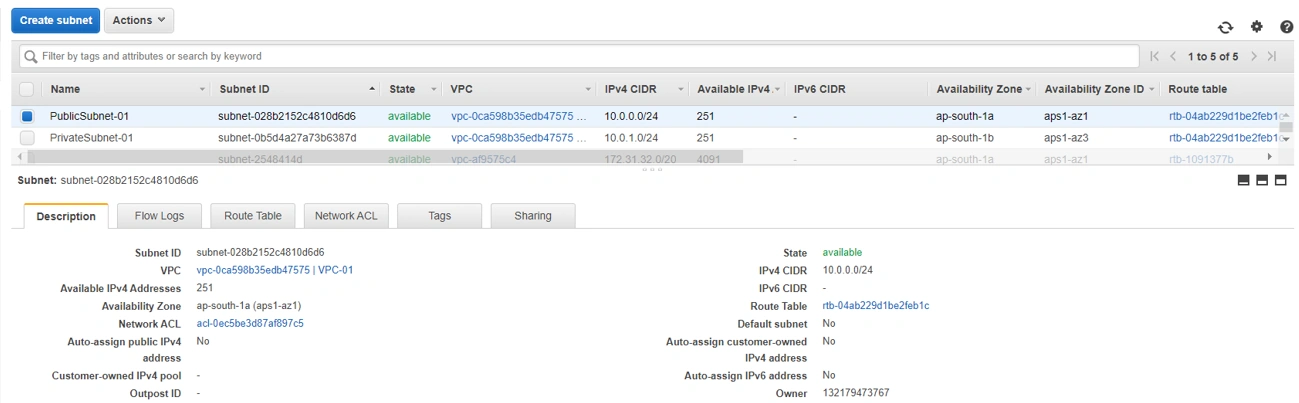
You can see both of the subnets shown in the list as of now these are only given names public and private, lets make them public and private subnets actually in the next steps
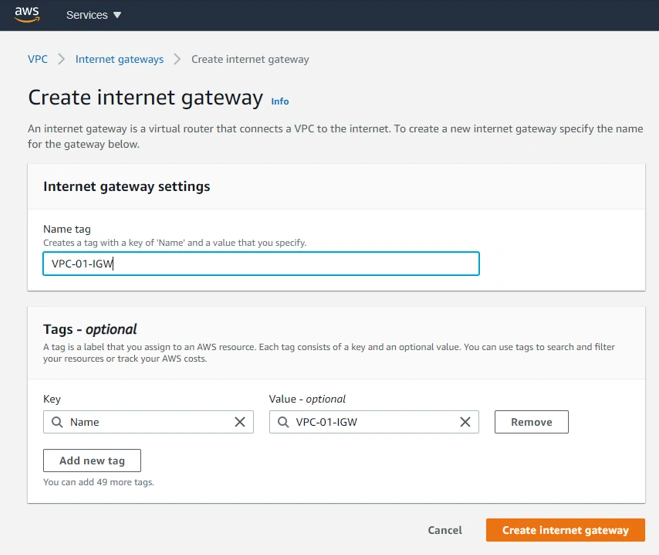
Create Internet Gateway – this will allow the communication between VPC and the internet so give the appropriate name tag here.
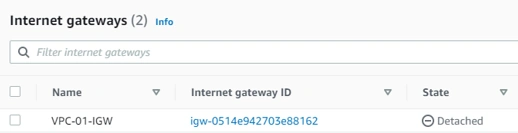
By Default, this internet gateway is not attached to any VPC
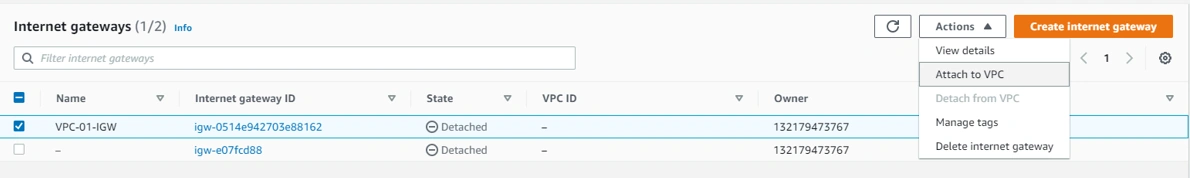
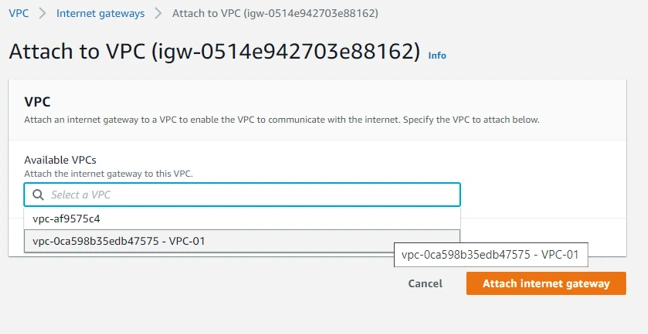
Let's attach the Internet Gateway to VPC by clicking on the Actions button and click to Attach to VPC.
Select the VPC that we create at the start and click on it to attach the internet gateway
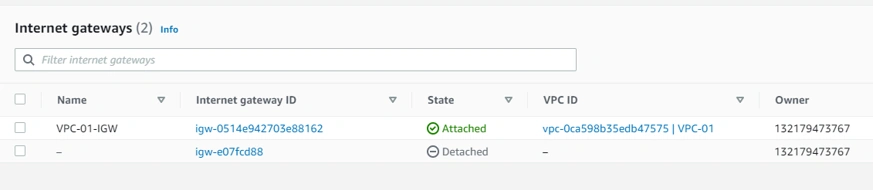
Now if you see in the list the VPC state changed to Attached and you can see the attached VPC id also.
Create and Define Route tables
Route table basically contains a set of rules which determines how and where the packets are directed over the internet, so we create this route table different for both public and private subnets
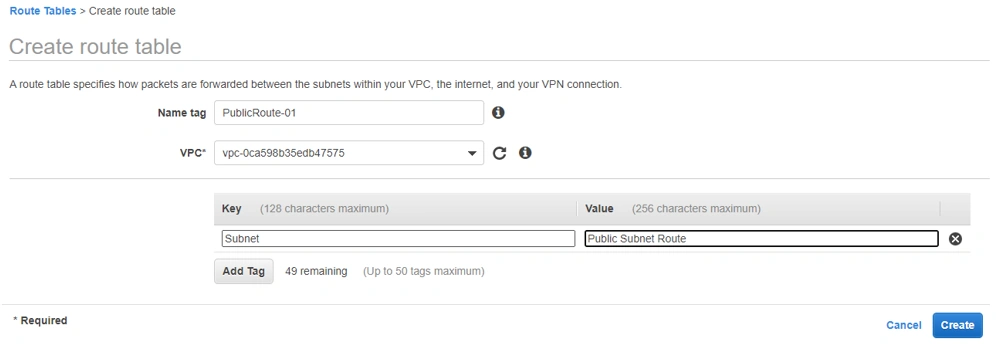
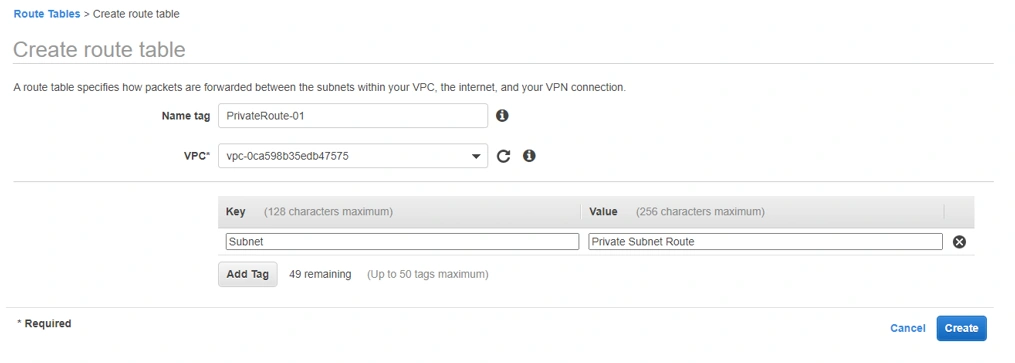
This route table will determine the subnet is a public or private subnet.
Associates Subnets and define routes
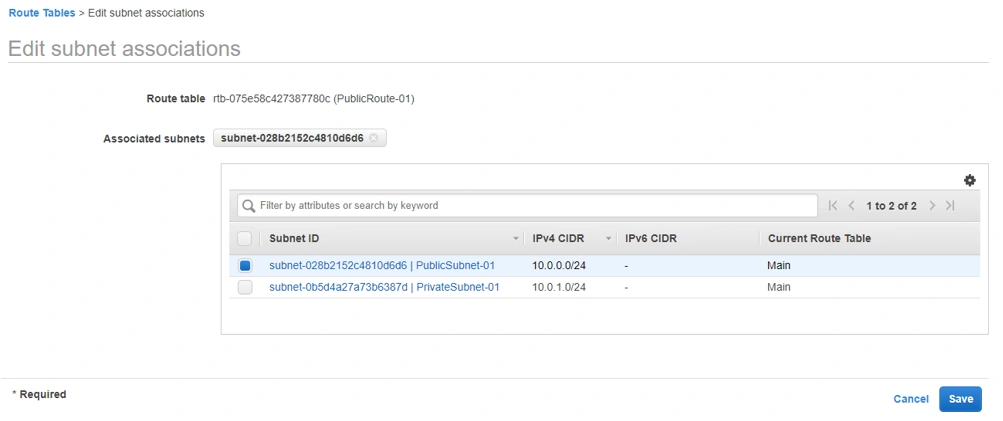
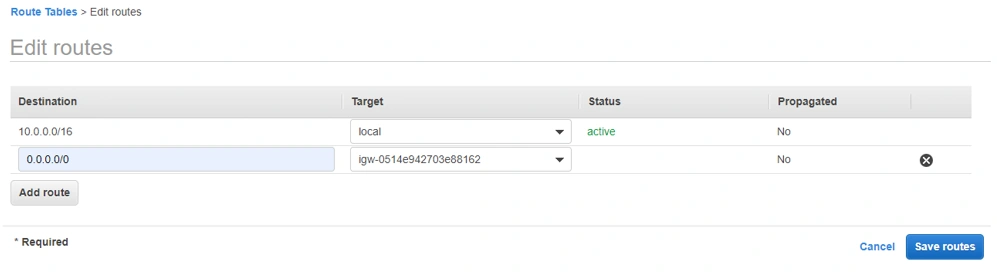
We will associate the public subnet with the Internet Gateway and edit the route to associate this with a created internet gateway, similarly, we will associate the private subnet with the NAT gateway as it will not allow the communication over the internet directly.
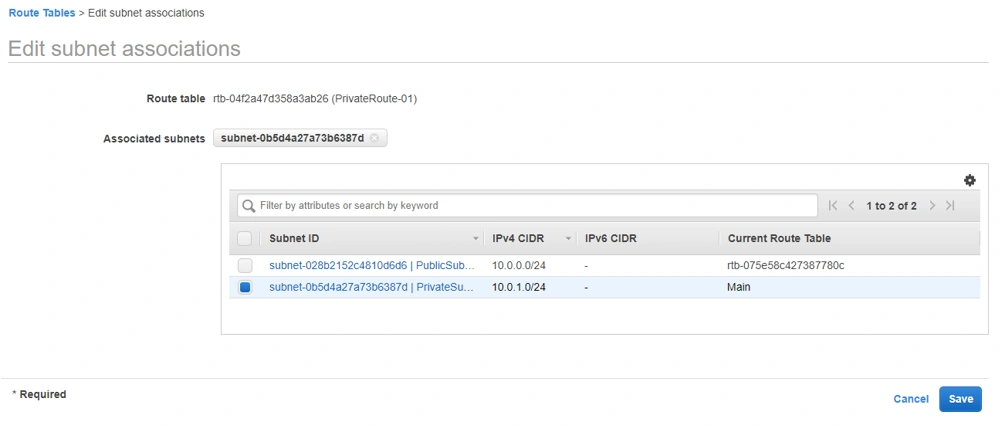
Private Subnet Association –
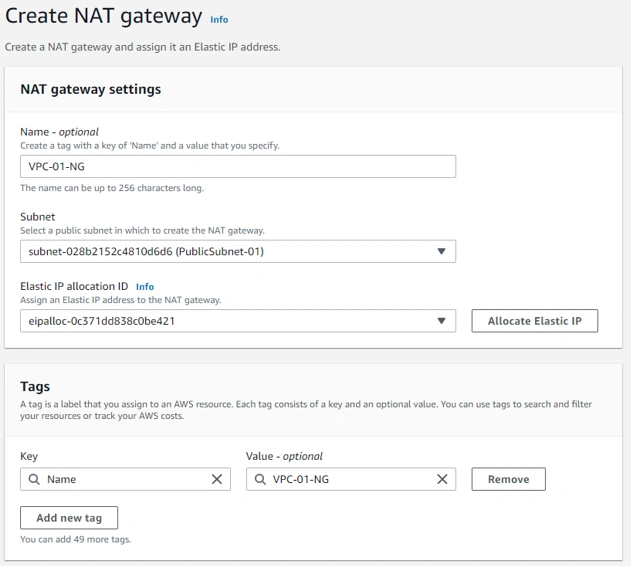
Create Nat gateway to define route for private subnet, as with this only there is communication possible so you can give a NAT gateway name and you have to allocate elastic IP separately so this IP will help you in the communication and also select the public subnet via which communication is possible.
This time we associate this NAT gateway with the private subnets so now our both public and private subnets are ready and we already associate the route table with them
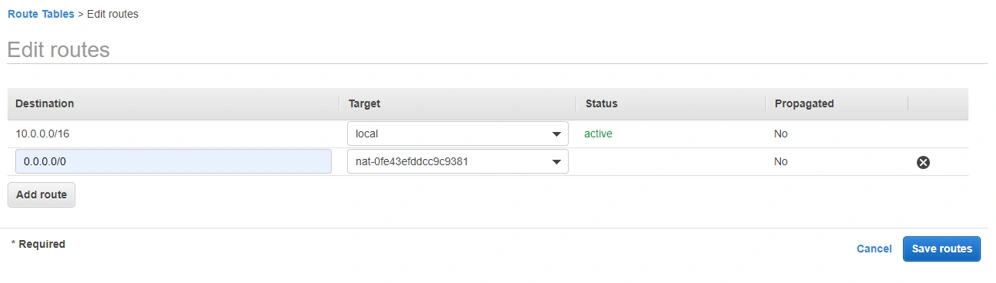
Time to create EC2 instance in both subnets
What is Amazon EC2 Instance
EC2 stands for Elastic compute cloud (Amazon EC2) and is one of the longest-running services on AWS. EC2 is just a virtual machine provisioned with a certain amount of CPU cores, memory, storage space, and networking. With this, anyone can install any type of operating system (OS) on it whether it's Linux or Windows.
Steps to create EC2 Instance
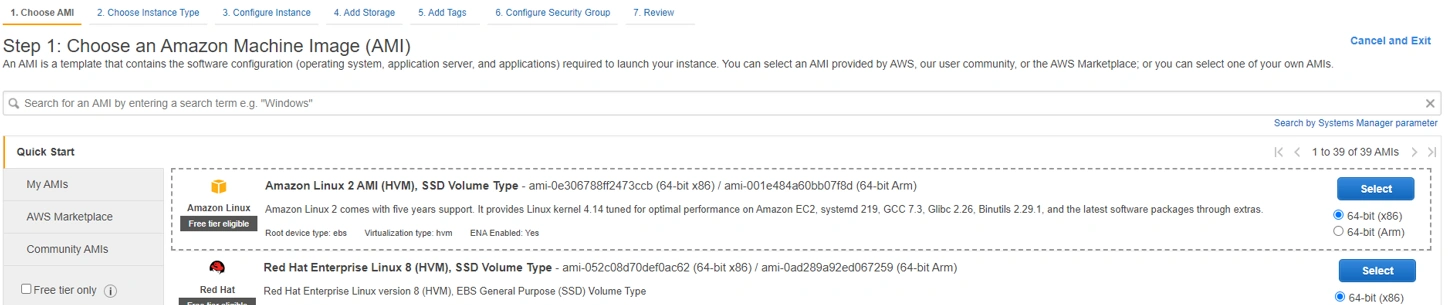
- Choose AMI
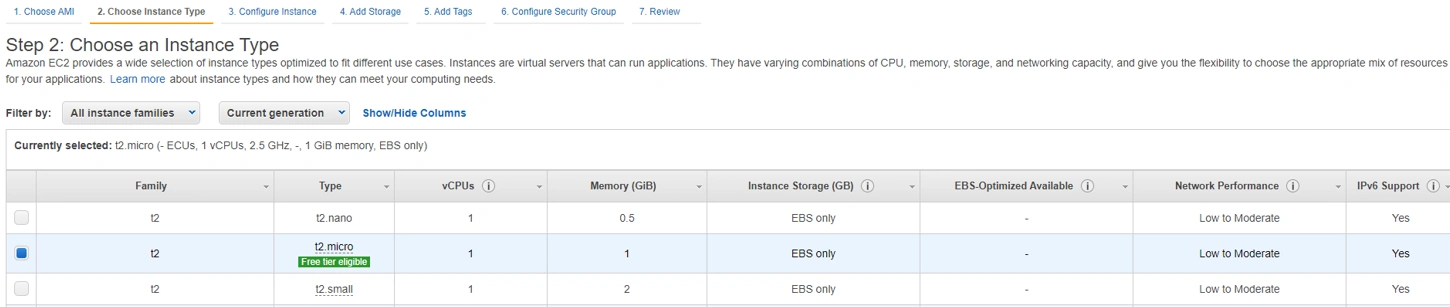
- Choose Instance Type
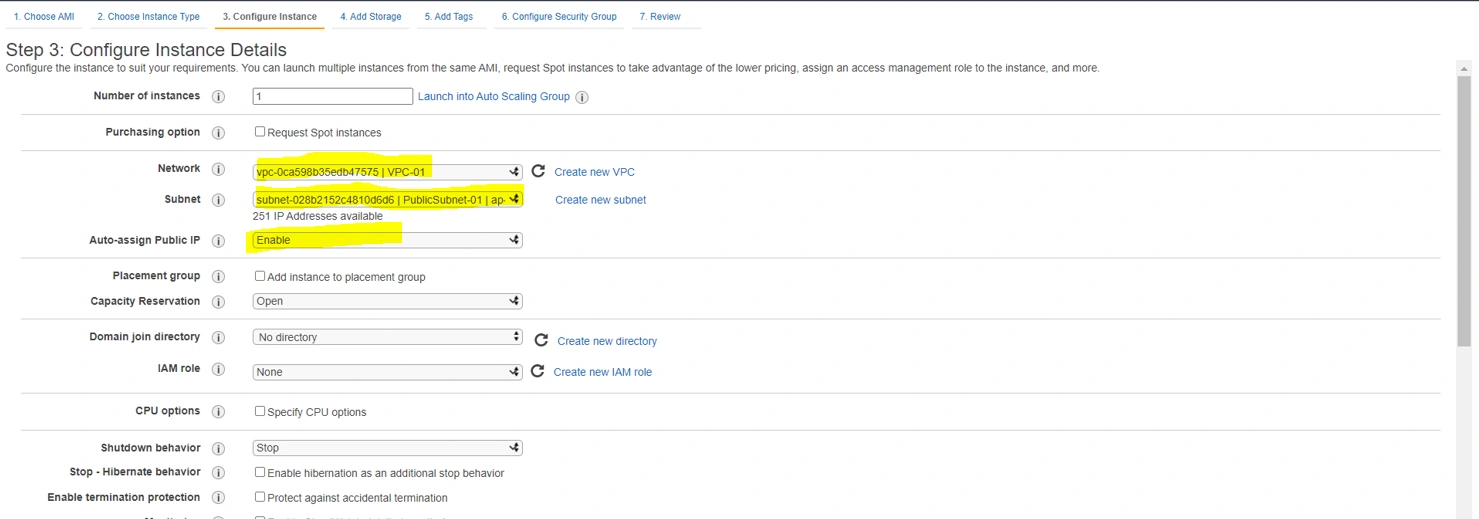
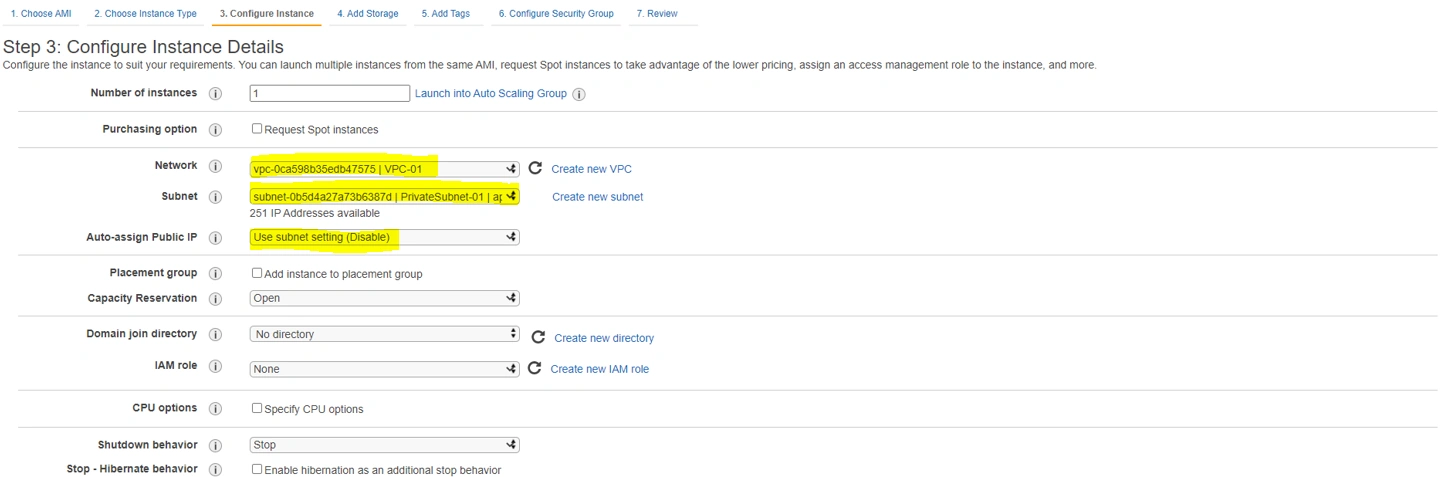
- Configure Instance
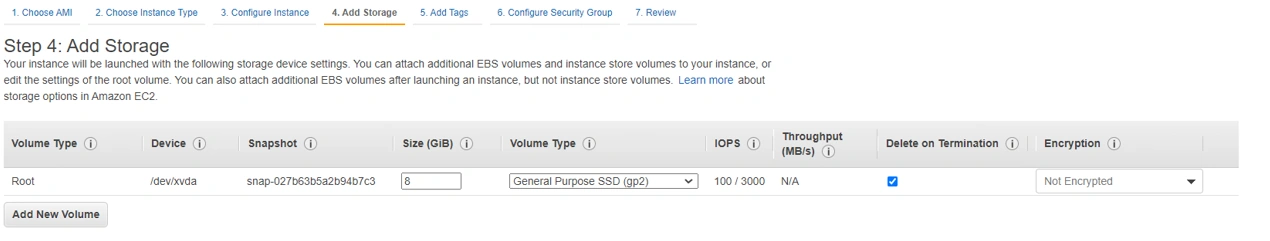
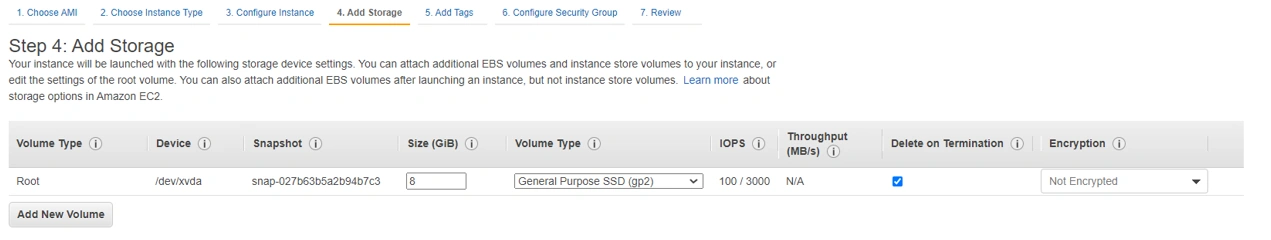
- Add Storage
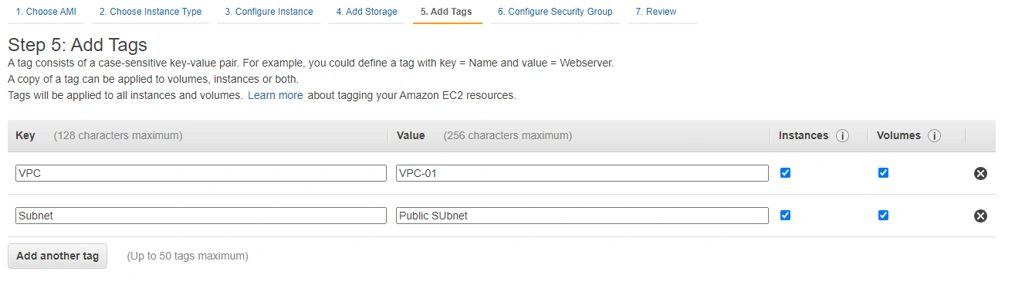
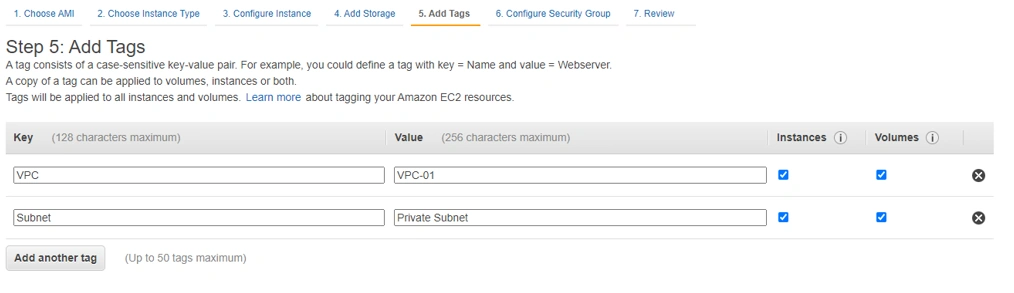
- Add Tags
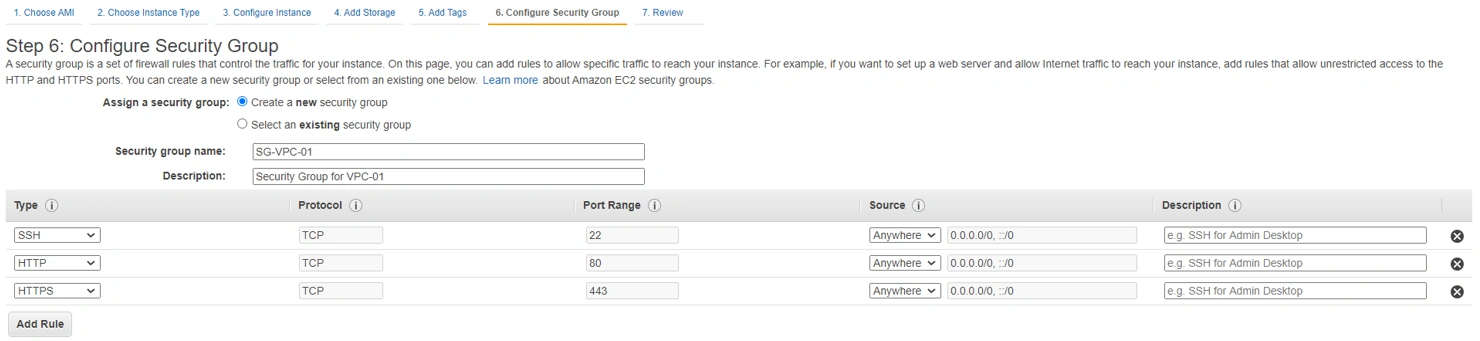
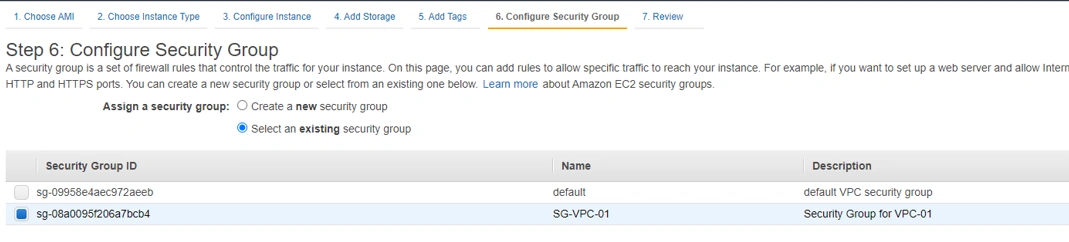
- Configure Security Group
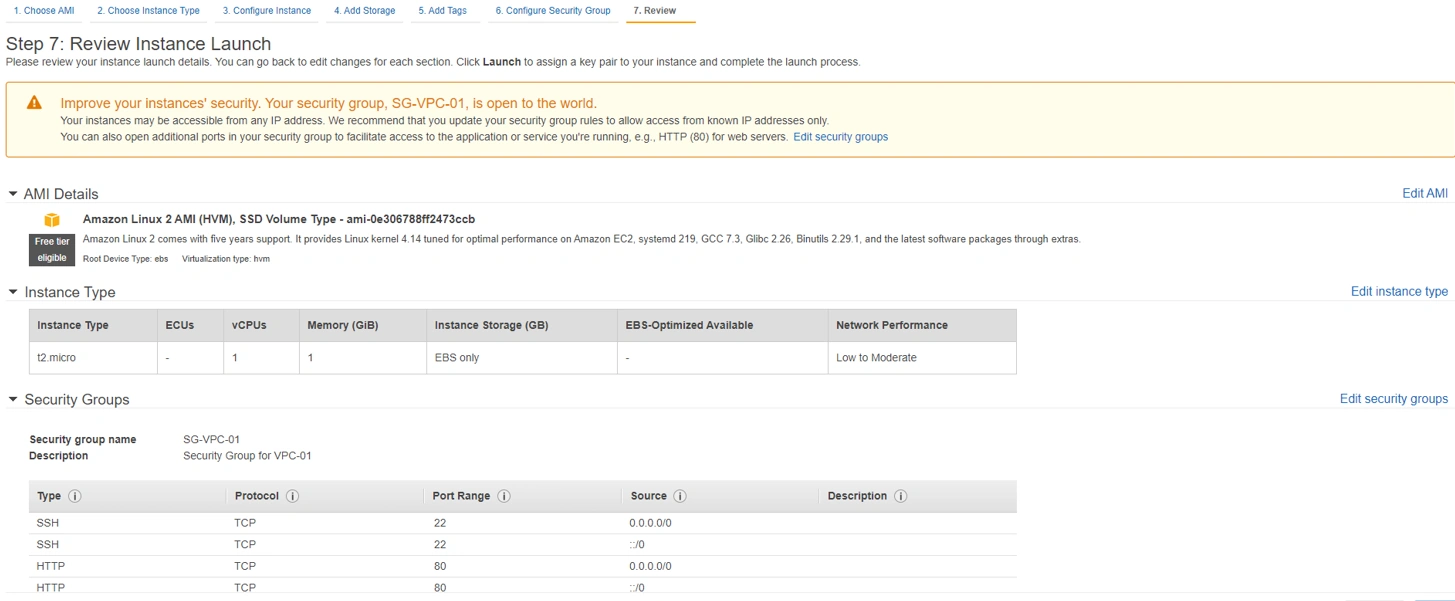
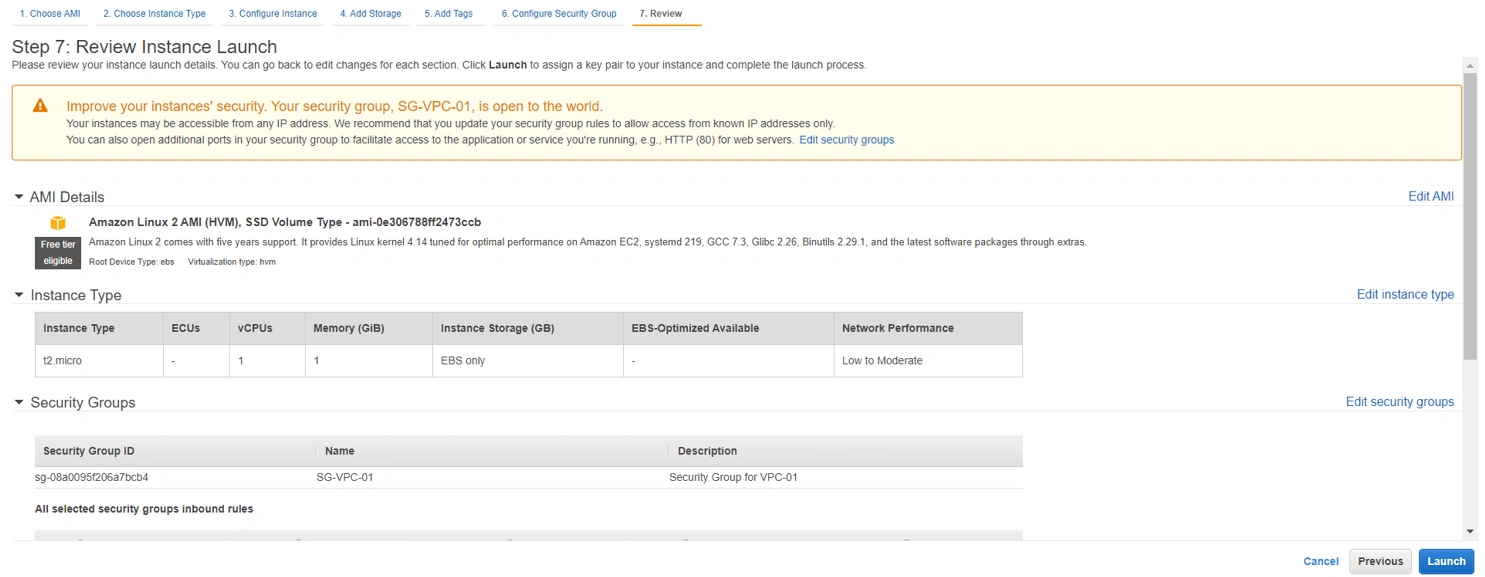
- Review
Public EC2 Instance –
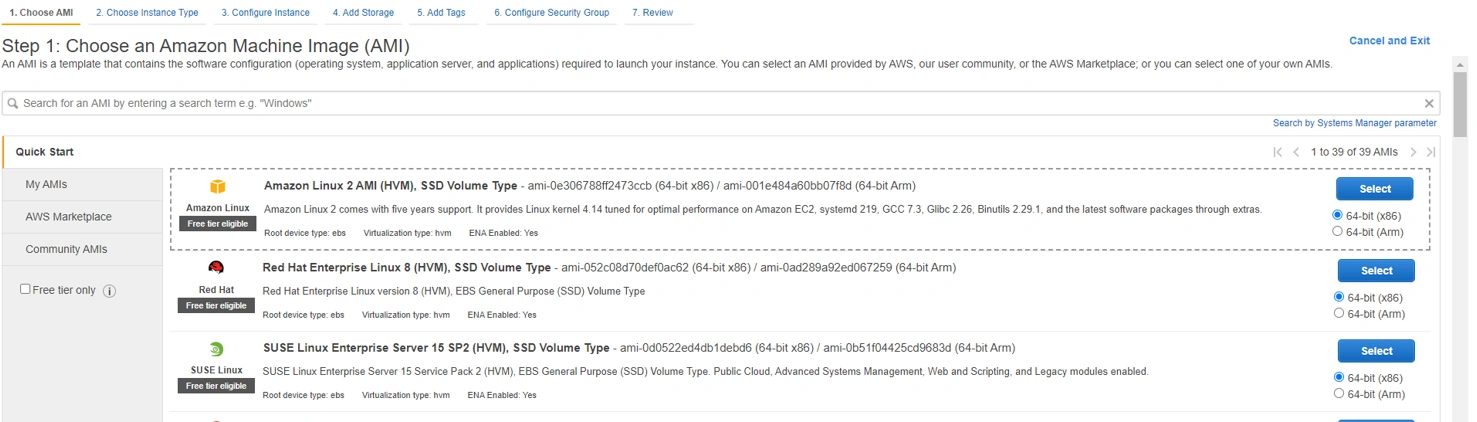
The first step is to choose the AMI means machine type whether you going to select Windows, Linux, or any other Machine.
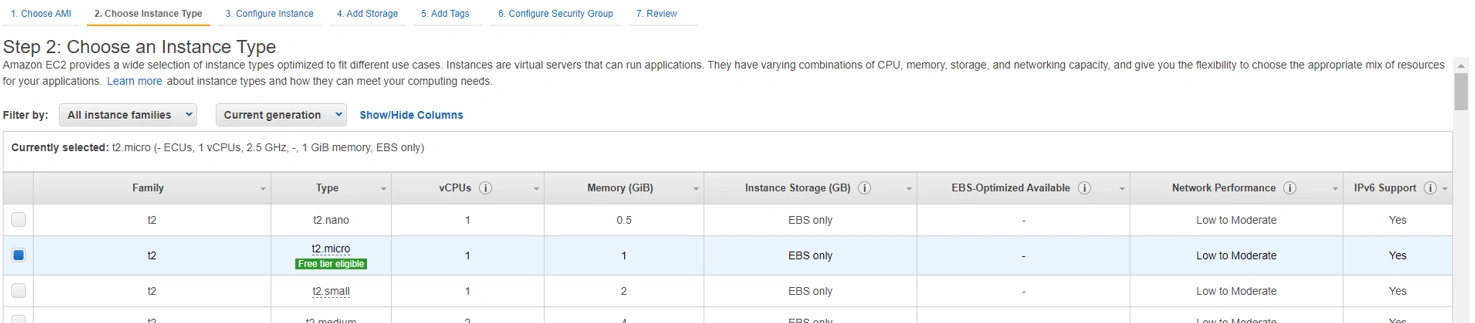
The next step is to choose our instance type which you select according to your requirement, I'm selecting here the free one t2.micro having 1 GB of memory and 1 CPU core
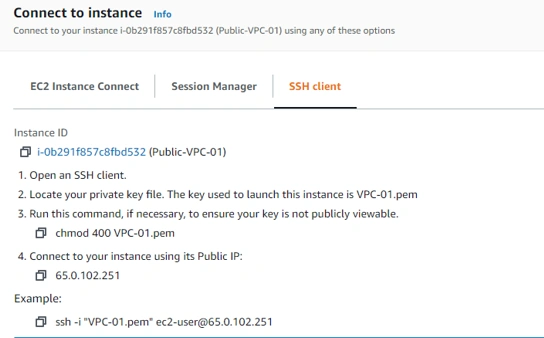
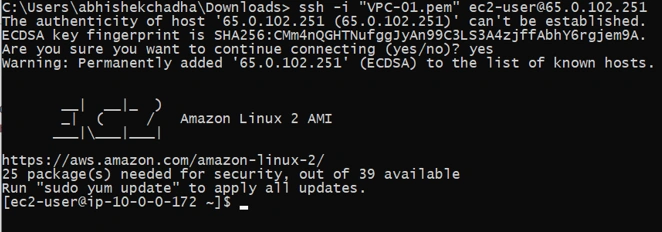
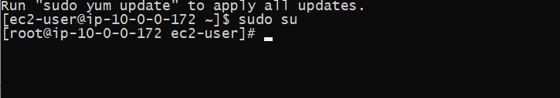
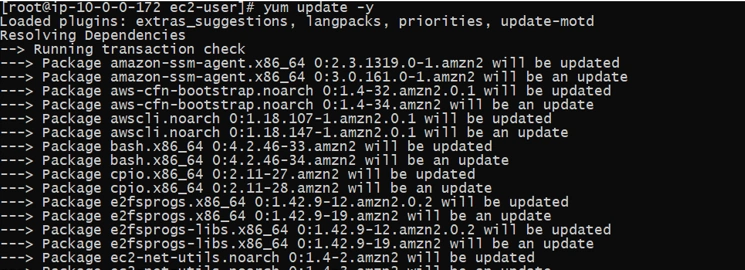

Join the conversation! Your thoughts help the community grow.