
Introduction
For an SSL/TLS socket connection from a client application to a server application, we need a server-side certificate. Client and server applications can communicate with each other via socket programming. In order to make sure the communication is secure/encrypted, we need to define a server certificate at the time of creating a server-side socket. This article describes a step by step procedure from scratch on how to generate a server-side X509 certificate on Windows 7 for SSL/TLS TCP communication using OpenSSL.
Note
This tutorial does not require any kind of Linux simulation or virtualization of Linux distribution on Windows. Instead, it describes how to generate the certificate solely on Windows. The procedure is tested on Windows 7 and it is assumed that the procedure will also work seamlessly for Windows 10 as well.
Overall, we first create a self-signed "Root key/certificate" pair. Then using this root key/Certificate, we create an intermediate Key/Certificate. Finally, we create a server certificate using the intermediate certificate. While creating a server certificate or server certificate signing request, we may consider using the "IP address" of the computer on which the server is running, as the “Common Name” field. Common Name is the mandatory parameter when running a certificate creation command of Openssl. This is due to the fact that some SSL programming libraries require that. I used the password “1234” whenever a password is required while creating a certificate or certificate signing request. As a result of each of the following steps of creating Key/Certificate/Certificate Signing Request, the corresponding Key/Certificate/Certificate Signing Request will be generated in its corresponding folder as per the directory structure given ahead.
1-Install/Setup OpenSSL
Download "Win32 OpenSSL v1.1.0f Light" from [3] and install it as mentioned at [2]. After installing Openssl, the path openssl.exe file should be added in the system path. That “oenssl.exe” can be run from our desired folder from the command prompt.
2-Setup Directory
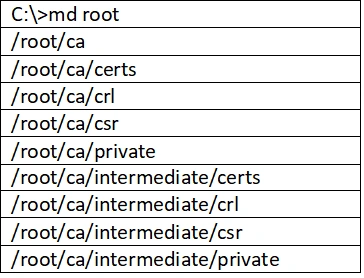
We will create a "\root" folder at C:\ and the following folder structure in the "\root" folder.
- Start Command Prompt
Start the command prompt; create a root folder and the following directory structure:
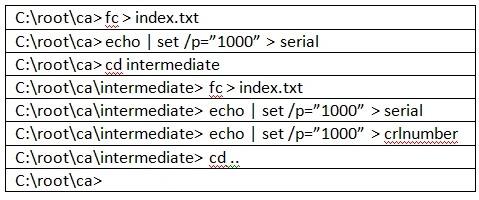
Do the following to get index, serial and crlnumber files in the appropriate folders
- Get Configuration files
Extract the root configuration file [4] from the attachment (configurationFiles.zip) and save it as “openssl.cfg” at C:\root\ca
For instance “C:\root\ca\openssl.cfg”
Extract the intermediate configuration file [5] from the attachment (configurationFiles.zip) and save it as “openssl.cfg” at C:\root\ca\intermediate
For instance "C:\root\ca\intermediate\openssl.cfg"
3-Certificate Creation Steps
- Set path at the command prompt
C:\root\ca> set RANDFILE=C:\root\ca\private\.rnd
C:\root\ca> set OPENSSL_CONF=C:\root\ca\openssl.cfg
- Start OpenSSL
C:\root\ca>openssl
openssl>
- Create a Root Key
openssl> genrsa -aes256 -out private/ca.key.pem 4096
- Create a Root Certificate (this is self-signed certificate)
openssl> req -config openssl.cnf \ -key private/ca.key.pem \ -new -x509 -days 7300 -sha256 -extensions v3_ca \ -out certs/ca.cert.pem
- Create an Intermediate Key
openssl> genrsa -aes256 \ -out intermediate/private/intermediate.key.pem 4096
- Create an Intermediate certificate signing request
openssl> req -config intermediate/openssl.cfg -new -sha256 \ -key intermediate/private/intermediate.key.pem \ -out intermediate/csr/intermediate.csr.pem
- Create intermediate certificate (using Root Key/Certificate)
openssl> req -config openssl.cfg \ -key private/ca.key.pem \ -new -x509 -days 7300 -sha256 -extensions v3_ca \ -out certs/ca.cert.pem
- Quit OpenSSL
openssl> quit
C:\root\ca>
- Get CA-Chain Cert
C:\root\ca> type intermediate\certs\intermediate.cert.pem certs\ca.cert.pem > intermediate\certs\ca-chain.cert.pem
- Start OpenSSL
C:\root\ca>openssl
openssl>
- Create a Server Key
openssl>genrsa -aes256 \ -out intermediate/private/www.example.com.key.pem 2048
- Create a Server Signing Request
openssl>req -config intermediate/openssl.cnf \ -key intermediate/private/www.example.com.key.pem \ -new -sha256 -out intermediate/csr/www.example.com.csr.pem
- Create a Server Certificate (Using Server signing Request and Intermediate Certificate/Key)
openssl> ca -config intermediate/openssl.cnf \ -extensions server_cert -days 375 -notext -md sha256 \ -in intermediate/csr/www.example.com.csr.pem \ -out intermediate/certs/www.example.com.cert.pem
- Using Certificate
Now the SSL/TLS server can be configured with server key and server certificate while using CA-Chain-Cert as a trust certificate for the server. The Root certificate has to be configured at the Windows to enable the client to connect to the server.
4-Configure SSL/TLS Client at Windows
In order to enable the client to connect with the Server, we need to register the Root certificate (created in step 3.4) at the Windows machine from where the Client will access the Server. Do Step 4.1 and 4.2 to complete the Root certificate registration on the Windows machine.
- Go to the Control Panel
-> Credential Manager -> Add a Certificate based credential -> Open Certificate Manager
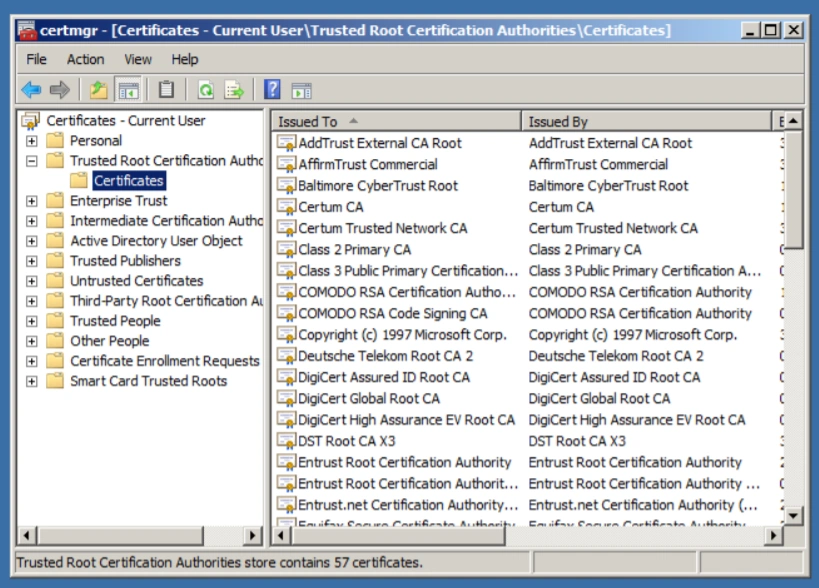
- Right Click on the Certificate
-> All Tasks -> Import -> Next -> Browse
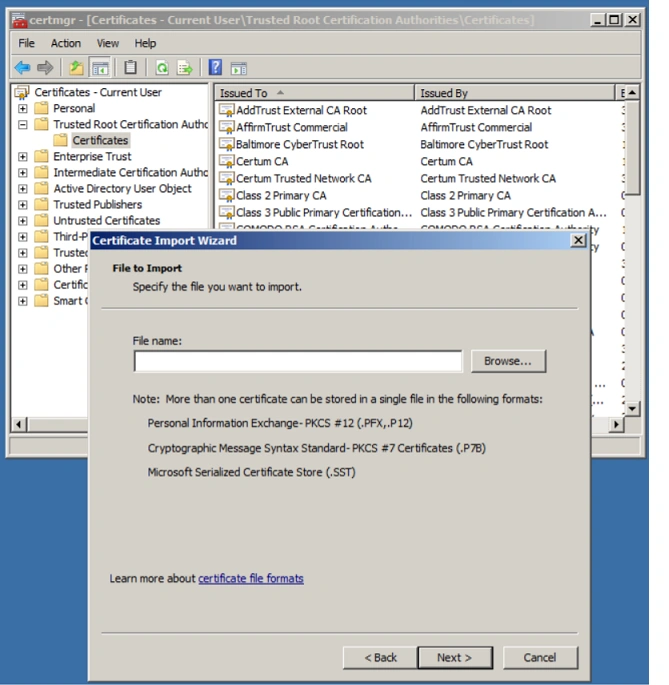
Browse the Root certificate that was generated in Step 3.4
References
Santa ClausPosted Jul 26, 2022, 2:32 PM
Junk article. Not only typo everywhere but logically broken. Comments even more wrong. You will end up with 2 Root CA instead 1 Root and 1 Intermediate. Worst Cyber Security professional ever, hope he change occupation field for good
Sebastian LaufPosted Apr 29, 2022, 10:53 AM
Step 3-7 - use this - then it works : req -config intermediate/openssl.cfg -key intermediate/private/intermediate.key.pem -new -x509 -days 73000 -sha256 -extensions v3_ca -out intermediate/certs/intermediate.cert.pem
Sebastian LaufPosted Apr 29, 2022, 10:41 AM
How to get intermediate.cert.pem ? step 3-7 doesn't create this file !
Yves DuenowPosted Dec 13, 2021, 8:38 AM
Is it too hard to verify the steps before posting such an article? its a pain to run into lazy errors like .cfg and .cnf. Step 13 still was not corrected though comments told about the problem. Step 7 is the same as step 4? And wont create an intermediate certificate. Maybe it was meant to be: ca -config openssl.cfg -days 7300 -notext -md sha256 -in intermediate/csr/intermediate.csr.pem -out intermediate/certs/intermediate.cert.pem as the correction in the comments also wont work and wont create a signed certificate
Jouni LahtinenPosted Nov 18, 2021, 11:19 AM
Errors in the article and doesnt work
ashishPosted Jun 21, 2021, 6:50 AM
Nice article! but Getting error at step 9 the system can not find the file specified intermediate\certs\intermediate.cert.pem. Could you please help
Uemit KocPosted Jun 20, 2021, 11:41 AM
Hello Jamil, I followed the instructions. Everything worked out fine. But at step 13 "Create a Server Certificate (Using Server signing Request and Intermediate Certificate/Key)" , when entering the command, I get the following error message: CA certificate and CA private key do not match17312:error:2807106B:UI routines:UI_process:processing error:crypto\ui\ui_lib.c:545:while reading strings 17312:error:0B080074:x509 certificate routines:X509_check_private_key:key values mismatch:crypto\x509\x509_cmp.c:303: error in ca
supriya takPosted Feb 10, 2021, 12:04 PM
Req -config openssl.cnf \ -key private/ca.key.pem \ -new -x509 -days 7300 -sha256 -extensions v3_ca \ -out certs/ca.cert.pem not working OpenSSL> req -config openssl.cnf \ -key private/ca.key.pem \ -new -x509 -days 7300 -sha256 -extensions v3_ca \ -out certs/ca.cert.pemunknown option \
Luke McCarthyPosted Jan 18, 2021, 6:35 PM
Hi Jamil, thanks for the notes with the updates from the comments I have created the certificates I successfully but am struggling to use them in my application. Can you confirm which certificates should be imported where in the certificate manager?
Michael BowersPosted Nov 19, 2020, 11:22 AM
What does "fc > index.txt" do?
jay sawantPosted Nov 2, 2020, 1:39 PM
Followed your steps, failing at 3.13. Can you elaborate the step 3.13?