
Introduction
Have you faced a requirement when you need to test certificate-based authentication using the POSTMAN tool. If you have, then you are at the right place. In this article, we will go through the process of registering an Enterprise AD App using PowerShell and testing the application access using a Certificate using the POSTMAN tool.
Pre-requisites
You need to have.
- A Developer Subscription / Organization subscription
- Application Owner rights / Global Admin rights
- SharePoint Admin rights / Site Collection Admin access to a SharePoint Online site
Architecture
Below is the simple architecture of the application that we are going through in this article.
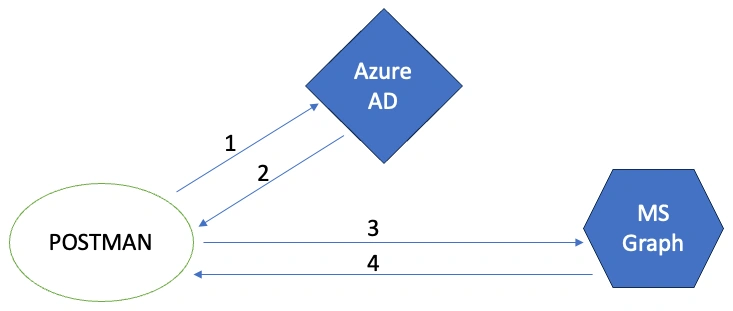
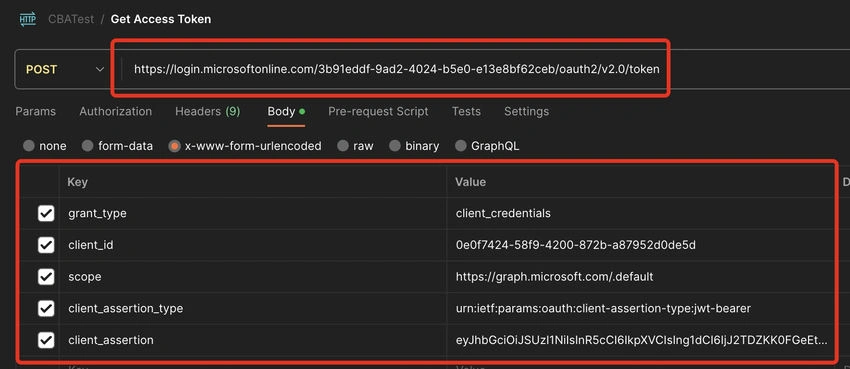
- Postman sends a request to the Azure AD token endpoint.
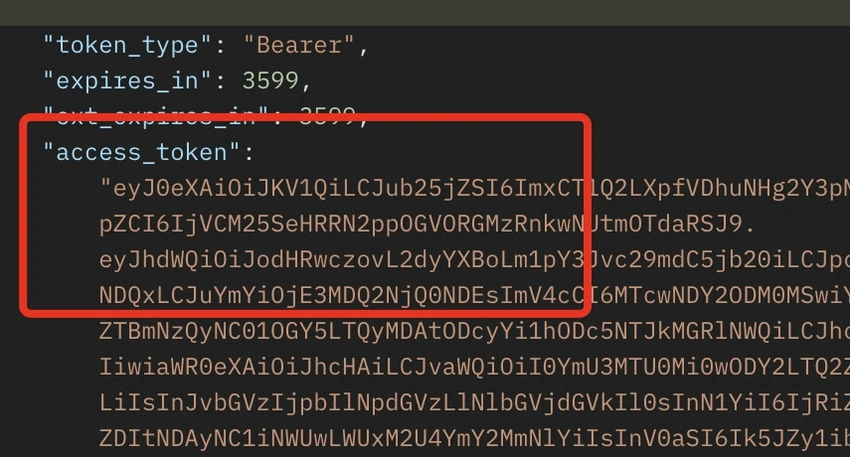
- Postman acquires tokens from Azure AD.
- Postman passes the request to MS Graph with a token in the header.
- Postman receives a response from MS Graph.
Creating an App in Azure
Step 1. Run the PS Script for App registration. For Enterprise AD App creation, we are using the PowerShell script to do that. At first, we define the parameters and then run the Register-PnPAzureADApp command and get the certificates saved in a local folder. Below are the lines of the PS Script.
$AppRegistrationName = "CBATestApp"
$TenantName = "5wrdjv.onmicrosoft.com"
$SPOAdminUrl = "https://5wrdjv-admin.sharepoint.com"
$CertPasscode = Read-Host -AsSecureString -Prompt "Enter Passcode"
Connect-PnPOnline -Url $SPOAdminUrl -Interactive
Register-PnPAzureADApp -ApplicationName $AppRegistrationName -Tenant $TenantName -OutPath "/Users/vinaydeepayinapurapu/Desktop/VinayWorkingDocs/PowerShell/Certs/CBATest/" -CertificatePassword $CertPasscode -SharePointApplicationPermissions Sites.Selected -Interactive
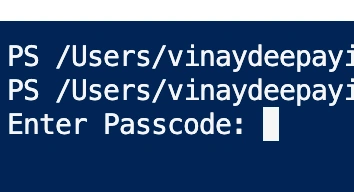
Note. During this script execution, you will be prompted for the passcode, which is needed to encrypt the Self-signed certificate. Please save the passcode for extracting Public and Private keys.
Step 2. Choose the account or enter the credentials. After entering the password, in the interactive mode, you might be asked to enter the credentials, the email ID that has an M365 developer subscription, or with organization email as mentioned in the pre-requisites. In this case, I have an M365 developer subscription and an account with Global Admin rights.
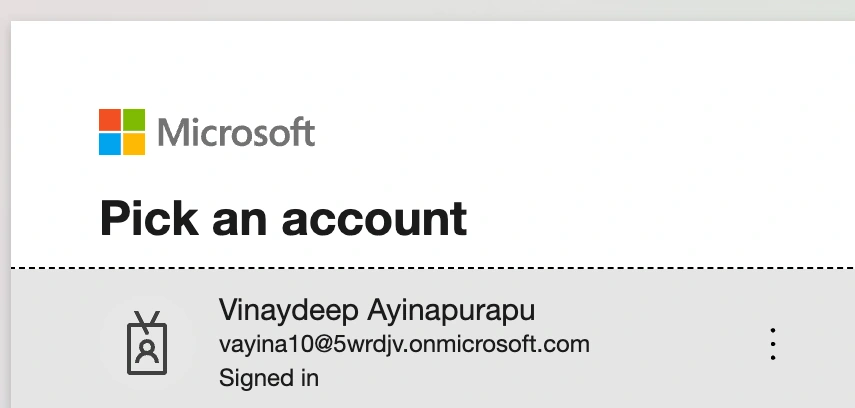
On successful authentication, you will be getting a message, successfully acquired Auth token.
Step 3. Grant Consent. It will take another 30 seconds to run the consent flow. This time, it checks the scope for which the AD app has been requested and asks for admin consent that needs Global / Tenant admin consent before provisioning.
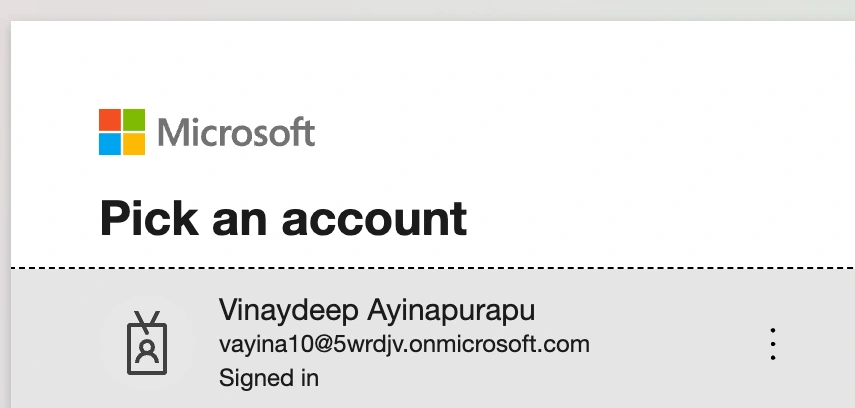
Pay attention to the requested scopes. If your account does not have Global Admin rights, you need to work with your Global Admin to grant the consent for the requested scopes. In the screenshot below, the app requests to.
- Signin and read the user profile
- Access to Specific Site Collections.
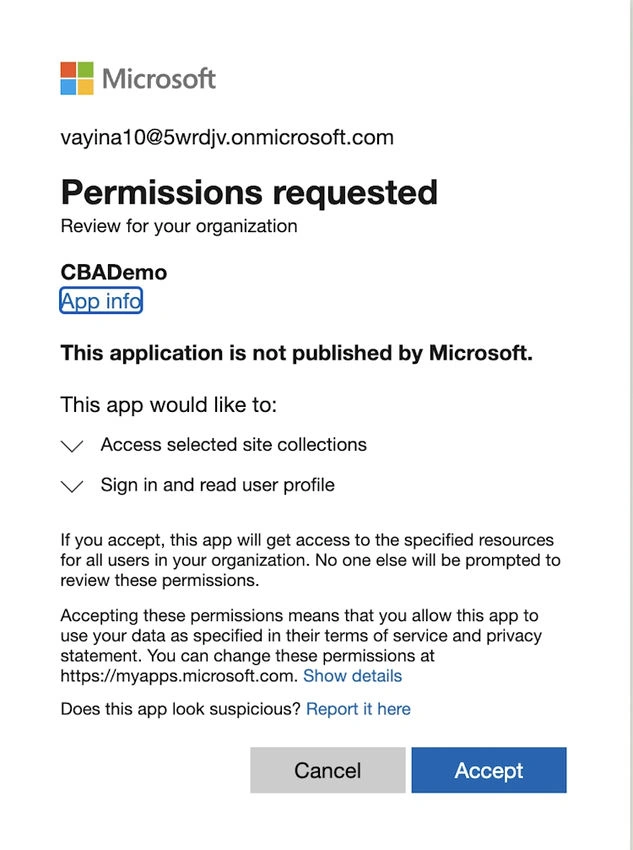
Once you click on ‘Accept’ another window appears that says you consented to the Azure AD App.
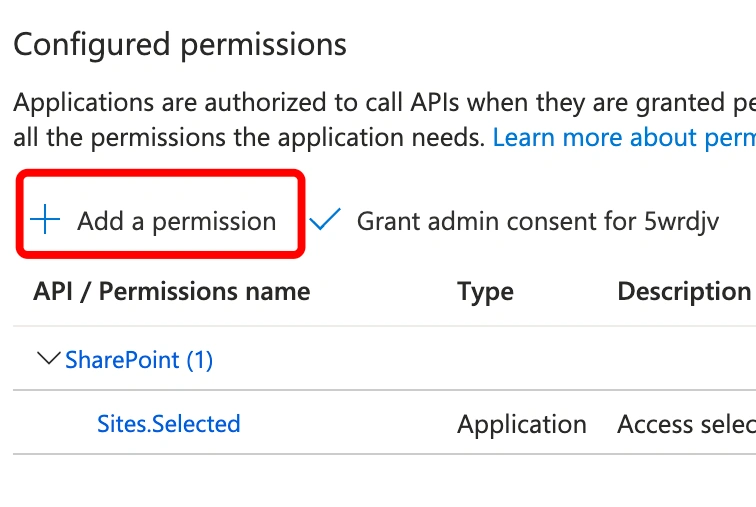
Step 4. Validate the API permissions in Azure Portal. You can also log in to the Azure Portal (https://portal.azure.com) Microsoft Entra App registrations and search for newly created apps. Check the ‘Api Permissions’.
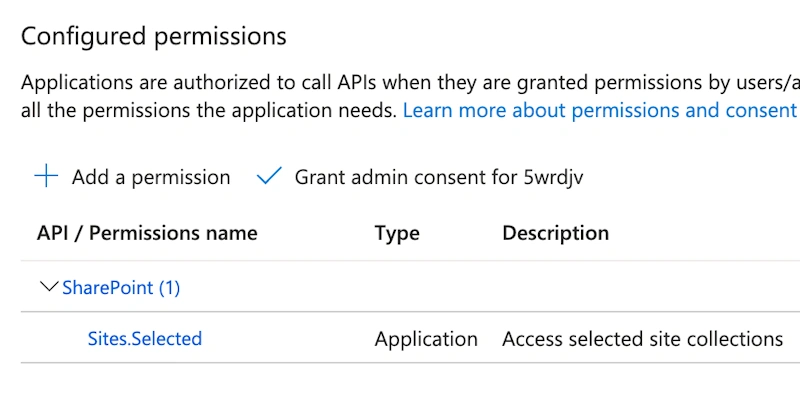
Step 5. Add the ‘Graph’ API permissions for scope ‘Sites.Selected’. This is needed to check the Graph API calls via POSTMAN using Certificate-Based Authentication.
Select ‘Microsoft Graph’
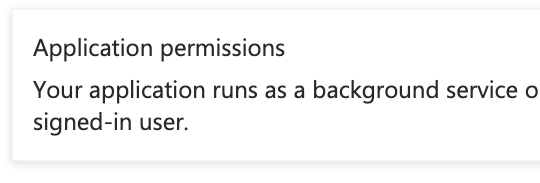
Select ‘Application Permissions’ Tab.
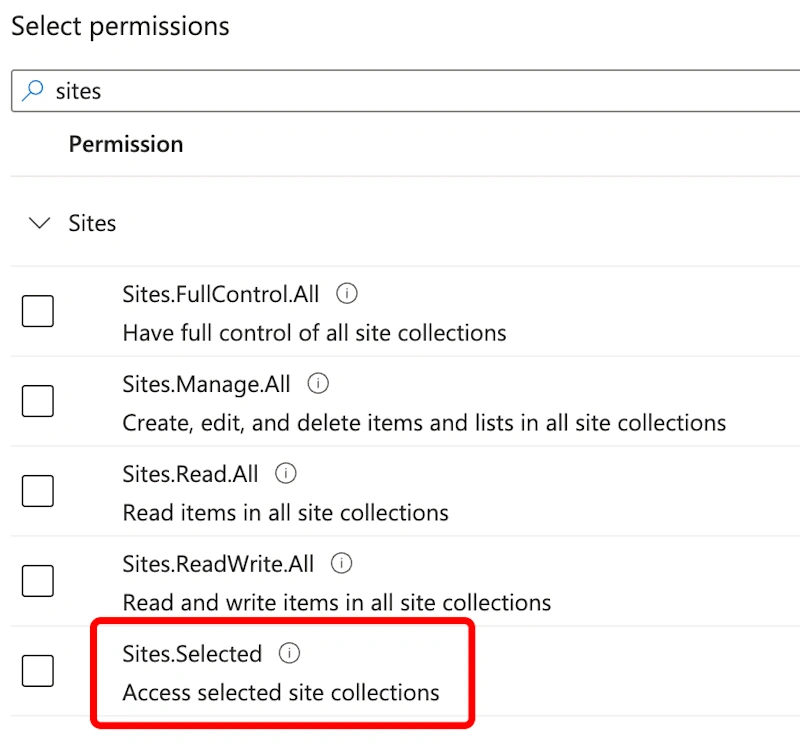
Search for ‘sites’ and then select ‘Sites.Selected’.
Finally, Grant ‘Admin Consent’ for the selected ‘Scopes’.
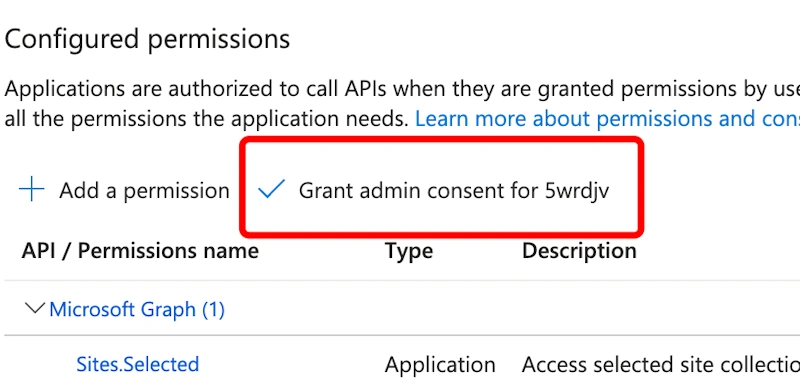
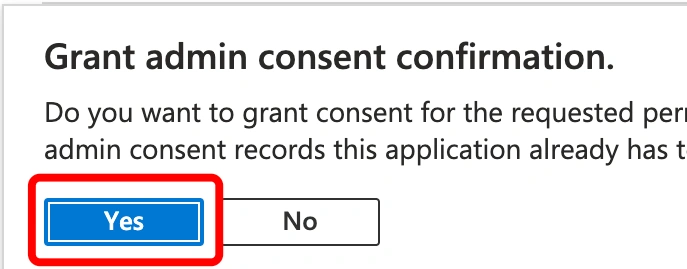
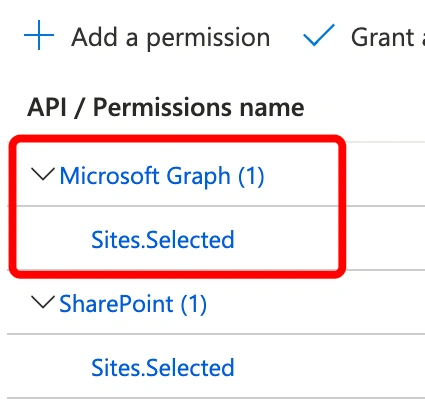
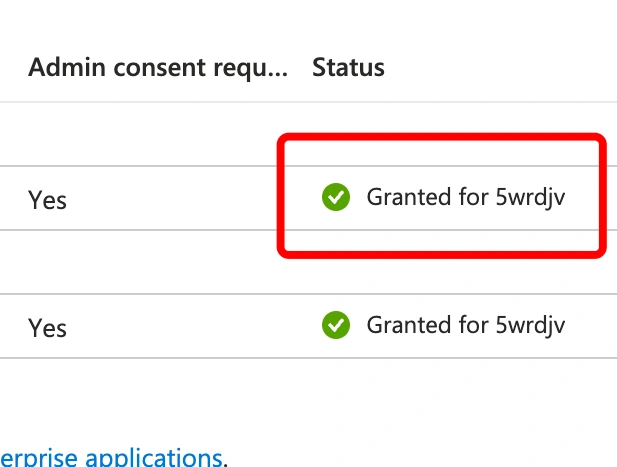
You should be able to see a green tick after admin consent has been granted, just like the screenshot below.
Step 6. Validate the generated certs. Once the App is registered, you should see the below files in the folder where the path is mentioned in the PowerShell -OutPath parameter.
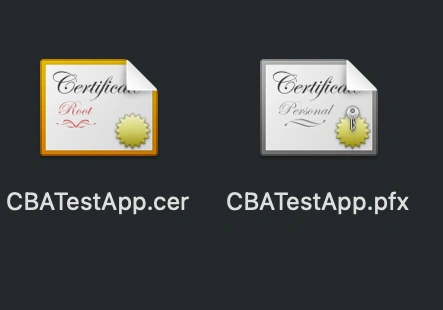
- .cer file: Public key file imported to Azure AD Certificate section, and in turn, you will get thumb print.
- .pfx file: private key file used to authenticate with the App and get access token with defined scopes.
Extracting the required values
Once the app is created and the certificates are available in your local folder, it is required to extract certain values.
- Public key in pem format
- Private key in pem format
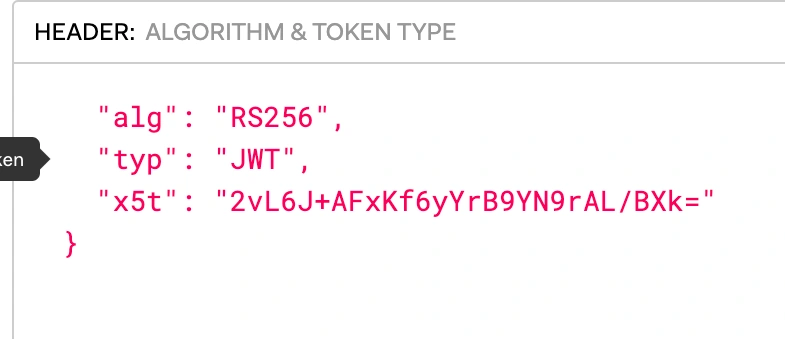
- Thumbprint in base 64 encoded format
Note. PEM stands for privacy-enhanced mail, which is the format used to encode the certificates. More about the PEM can be found in the references section.
Getting Private key in PEM format
For this, you will use the pfx certificate that is generated during the app creation using the PowerShell command Register-PnPAzureADApp and the ‘openssl’ command.
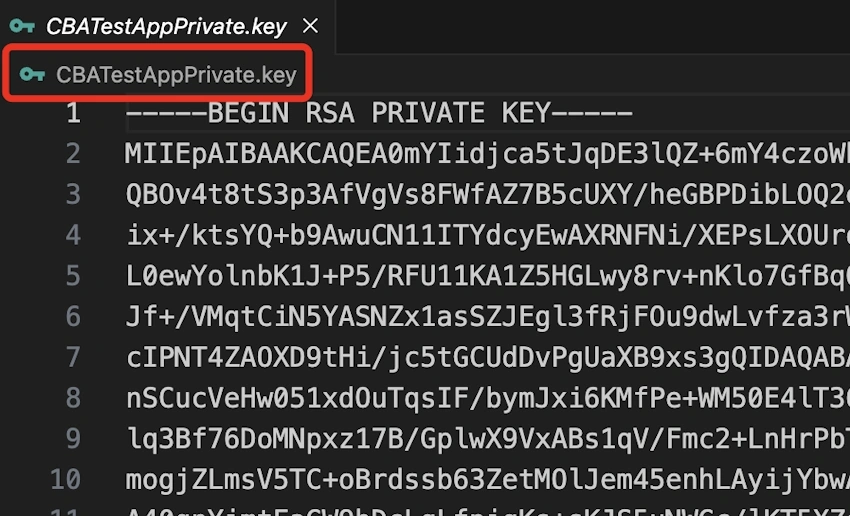
openssl pkcs12 -in CBATestApp.pfx -nodes -nocerts | openssl rsa -out CBATestAppPrivate.key
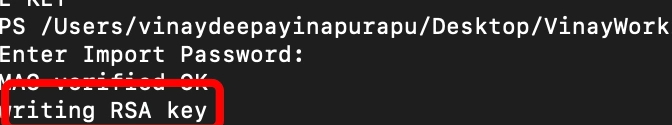
Note: You will be asked for an import password. Enter the passphrase that was entered during the Azure AD App creation.
Getting Public key in PEM format
After getting the Private key, you can extract the public key using openssl by entering the below command.
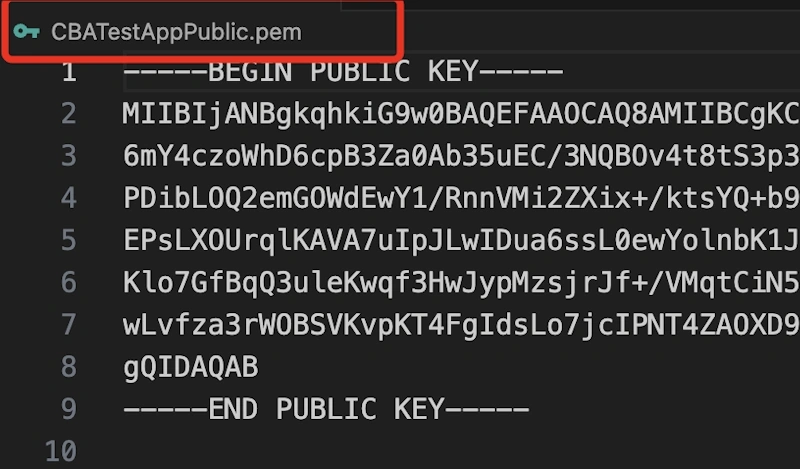
openssl rsa -in CBATestAppPrivate.key -pubout -out CBATestAppPublic.pem

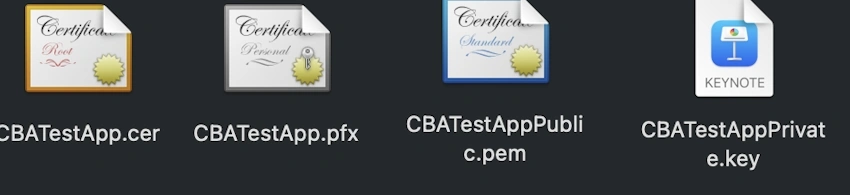
You would see the message ‘writing RSA key’. After that, you should see new public and private keys. In this case CBATestAppPublic.pem, CBATestAppPrivate.key.
Getting x5t Claim
To get the certificate thumbprint, I used the Python code. Record the certificate Thumbprint during the App creation and then supplement the Thumbprint in the below Python script to get the x5t claim.
import binascii
import base64
thumbprint_hex = 'DAF2FA27E005C4A7FAC98AC1F5837DAC02FF0579'
thumbprint_binary = binascii.unhexlify(thumbprint_hex)
x5t_compliant = base64.b64encode(thumbprint_binary).decode('utf-8')
print(x5t_compliant)
Output
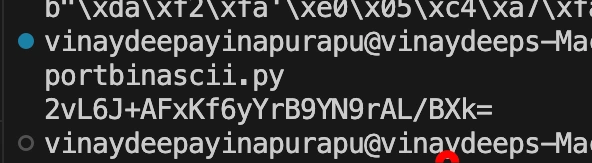
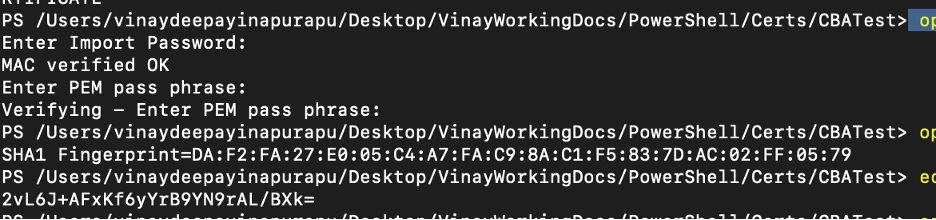
In this case the x5t claim is 2vL6J+AFxKf6yYrB9YN9rAL/BXk=
You can also use open SSL to get the x5t claim. Please follow the below steps
Step 1: Store all elements of chain of trust, using pkcs12 format and save as file .pem. Below is the command that needs to be run to extract the chain of trust from existing .pfx certificate.
openssl pkcs12 -in ./CBATestApp.pfx -out CBATestApp.pem
It will ask for password / passphrase that is used to to generate the root certificate from CSR (Certificate Sign Request).
Step 2: Once successful enter of passphrase, it will get the certificate in .pem format. Run the below command to get the certificate fingerprint / thumprint. It will be in SHA1 binary format.
openssl x509 -in ./CBATestApp.pem -noout -fingerprint
Step 3: SHA1 format is not supported in any of the certificate signing standards. We have to get the base 64 encoded thumbprint. For this we need to use sed. sed is linux based package, which lets you to search encode and delete the lines that matches a pattern without using a text editor. At the backend it uses regex. After you get the encoded value from SHA1 it is required to get hexadecimal dump which is supported by POSTMAN. For that we need to use openssl xxd. XXD is a command line tool that is used to get hexadecimal dump from binary format or vice-versa. Below is the command to get the final base64 encoded thumbprint.
Join the conversation! Your thoughts help the community grow.