
We need to install the following SDK for proceeding with further articles.
- Windows Identity Foundation SDK 4.0
The Windows
Identity Foundation is a framework for building identity-aware
applications. The framework abstracts the WS-Trust and WS-Federation
protocols and presents to developers APIs for building security token services
and claims-aware applications. Applications can use the framework to process
tokens issued from security token services and make identity-based decisions at
the web application or web service.
The SDK integrate with Visual Studio and provides templates to ease the tasks of developing Windows Identity based applications. We will be using this in the next article related to Access Control AppFabric.
Download
You can download the SDK using the following Url.
http://www.microsoft.com/download/en/details.aspx?id=4451
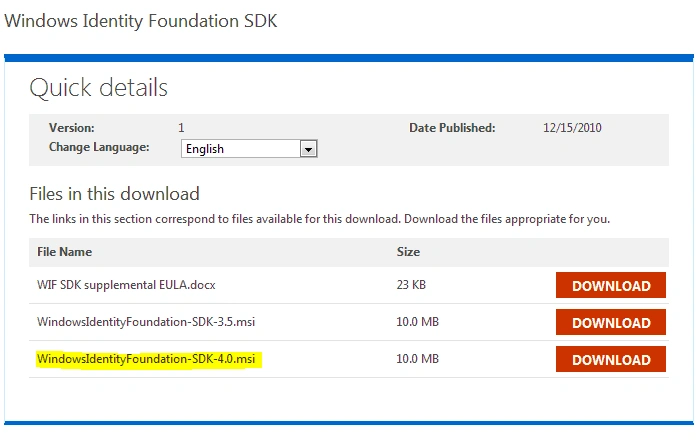
Download the appropriate version. For Visual Studio 2010, the 4.0 version is required.
Installation
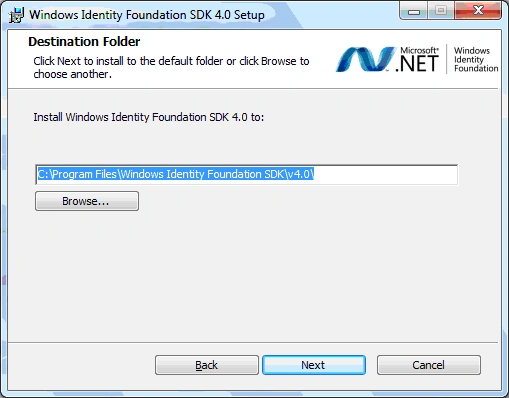
In the installation wizard please note the installation folder as it will be required in for future use.
Post Installation
Verification
We can verify whether the required Visual Studio extensions are installed. Open the Visual Studio and create an azure project with a web role in it.
Right click on the web role and you should be getting the following menu item named Add STS Reference. This is the Secured Token Service menu option which will perform necessary assembly reference and configuration change on execution.
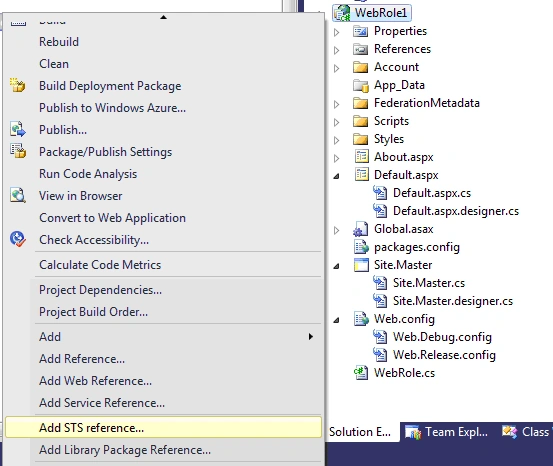
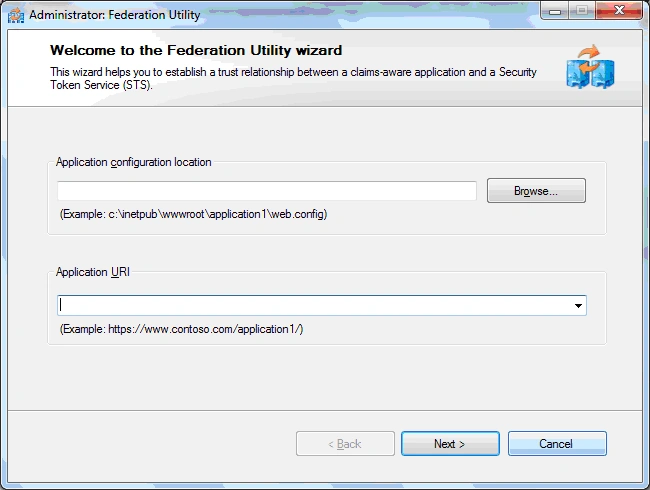
If you are able to see the following window, then the installation was successful.
Mohan PatilPosted Jan 14, 2018, 12:46 PM
@Jean Paul, I have developed claims aware application for my client. Client has provided me only metadata path. Using it I have configured the application using WIF Sdk and Metadata. But after login, I failed to read the claims because User as ClaimsPrincipal returns null.